

Sandbox and Test Environment Governance For Business Card API Integrations
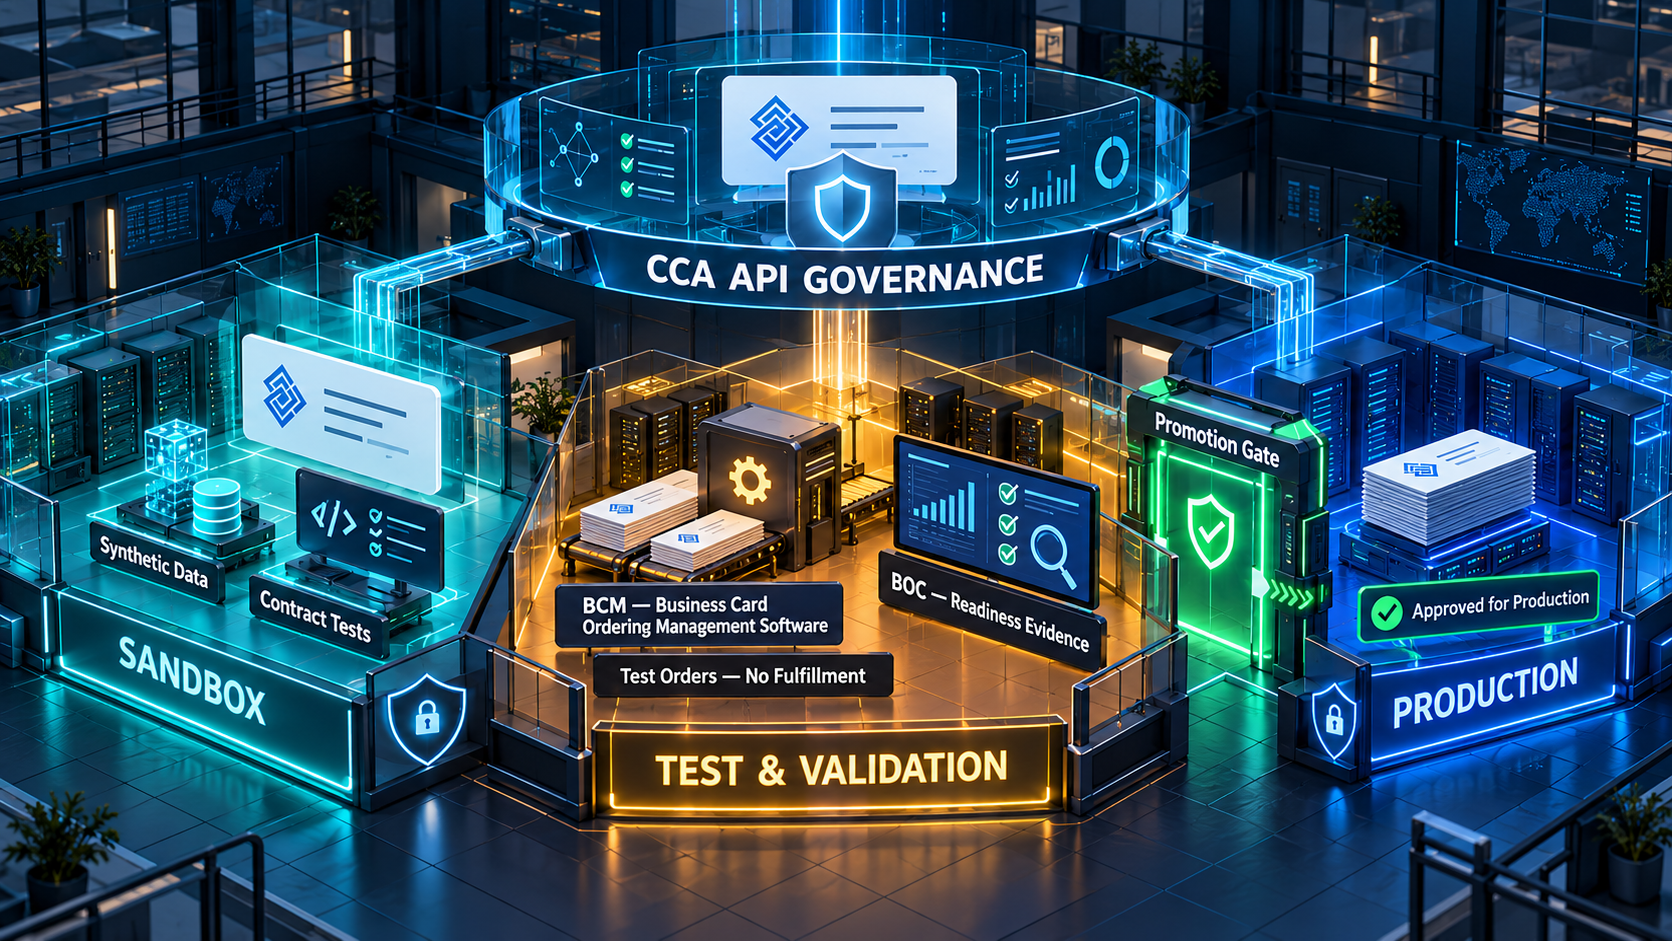
Proving integration behavior without exposing production identity or fulfillment. Isolate, simulate, validate, certify, promote.
A Sandbox Must Protect the Purpose of CCA
A sandbox gives integration teams room to learn contracts, validate mappings, exercise approvals, and recover from failures. It should accelerate delivery without becoming a lightly governed copy of production. If test identities can reach live employees, if test authorizations can create physical orders, or if production credentials work in a sandbox, the environment has failed its most important purpose.
Color Card Administrator (CCA) remains the authority for eligibility, identity fields, templates, approvals, quantities, destinations, and ordering rights in every environment. Business Card Manager (BCM) is the business card ordering management system or software that manages valid CCA-authorized orders. In nonproduction, BCM behavior should be simulated or safely isolated so no physical fulfillment occurs. Business Ops Center (BOC) oversees test exceptions, readiness evidence and controlled promotion.
Separate Environments by Authority, Not Just URL
Different hostnames do not create meaningful isolation if credentials, tenants, event routes or data stores remain shared. Each environment needs its own consumer identities, secrets, signing keys, tenant identifiers, quotas, logs, queues, and support procedures. Production access must never be the default fallback when a test dependency is unavailable.
The strongest design treats environment as an authorization boundary. Every request, token, decision, authorization, and event carries an environment context that cannot be overridden by a client parameter. The system cannot submit a sandbox object to production BCM, and [no one/the system] cannot replay a production authorization against a test endpoint.
Define the Environment Model
| Environment | Primary purpose | Data policy | Fulfillment behavior |
|---|---|---|---|
| Developer | Local contract and client behavior | Generated fixtures only | No BCM order creation |
| Shared integration | Cross-system workflow validation | Synthetic tenant data | Simulated BCM acceptance |
| Certification | Repeatable control and failure testing | Approved synthetic scenario library | Isolated BCM test order record |
| Preproduction | Production-like deployment verification | Masked only when formally approved | No physical fulfillment |
| Production | Authorized enterprise business activity | Governed live data | BCM manages valid authorized orders |
Use Synthetic Identity Records by Default
Test records should model the business conditions that CCA evaluates without copying real employee details. Create synthetic roles, legal entities, locations, languages, card programs, approval paths, and quantity limits. Use obvious non-real names or structural placeholders only when a display needs them; never reuse live phone numbers, email addresses, home addresses, or complete production card records.
Synthetic data needs governance because unrealistic fixtures create false confidence. Assign an owner, version, and expected outcome to each scenario. A fixture should state which source owns each field, which CCA rule applies, whether business card approval workflow is required, what authorization may be issued, and what BCM test outcome should follow.
Build a Policy Scenario Library
| Scenario family | Representative test | Expected CCA outcome | Downstream proof |
|---|---|---|---|
| Eligibility | Role and entity qualify for an approved program | Eligible or approval required | Allowed flow continues |
| Ineligibility | Worker type or status is outside policy | Denied with safe reason category | No BCM submission |
| Incomplete source data | Required governed field is absent | Incomplete data | Correction route displayed |
| Conflicting authority | CRM and HCM disagree on a locked field | Trusted source wins, or exception opens | No silent override |
| Template control | Requested design is inactive for the tenant | Denied or alternate approved template | Unapproved template never reaches BCM |
| Quantity control | Request exceeds role or program limit | Approval required or denied | Locked approved quantity only |
| Tenant isolation | Consumer requests another tenant record | Access rejected and recorded | No data exposure |
| Expired authorization | Previously valid approval is out of time | Reevaluation required | BCM rejects stale authorization |
Preserve Contract Parity Without Copying Production
The sandbox should use the same API shape, required headers, error model, idempotency behavior, event envelope, and supported version rules as production. Differences should be documented as environment capabilities, not hidden contract variations. A consumer that passes only because the sandbox accepts extra fields or skips validation is not production-ready.
Parity does not require identical infrastructure scale or live integrations. It requires the same externally observable enterprise vendor governance semantics. CCA should make the same category of policy decision for the same versioned synthetic scenario, BCM simulation should enforce the same authorization boundary, and BOC evidence should use the same correlation model.
Disable Physical Fulfillment by Design
Nonproduction environments should not depend on a warning label or a tester remembering not to ship. Remove provider routes, use non-routable destination patterns, reject live account identifiers, and mark every test authorization with an environment-bound claim. The BCM test instance should create a traceable simulated order record without transmitting production work.
If the business requires a limited end-to-end production proof, govern it as a separate controlled exercise with explicit authorization, known recipients, limited quantities, and reconciliation. It should not be called a sandbox test, and its credentials or routes should not remain available after the exercise.
Test the CCA to BCM Boundary
| Test | CCA evidence | BCM test behavior | Failure to reject |
|---|---|---|---|
| Valid authorization | Locked fields, scope, expiry and correlation | Accept once and return test order ID | Unscoped order creation |
| Repeated submission | Same authorization and idempotency context | Return existing test order result | Second order for same intent |
| Altered payload | Digest or field mismatch | Reject without creating order | Consumer editing approved values |
| Expired authorization | Expiry is in the past | Reject and preserve evidence | Graceful acceptance outside policy |
| Wrong environment | Environment claim does not match endpoint | Reject before processing | Cross-environment object reuse |
| Unknown outcome | Acceptance response is suppressed | Remain queryable by correlation | Blind replacement order |
Exercise Negative and Destructive Cases Safely
A certification environment should make failure testing routine. Teams need to test invalid signatures, missing scopes, malformed requests, quota responses, delayed approvals, duplicate events, out-of-order webhooks, unavailable dependencies, and unknown order outcomes. These conditions are difficult to test safely when they can affect real employees or fulfillment.
Fault injection must remain bounded. Define which dependency something/a failure may delay or fail, who may start the exercise, how long it can run, and how the environment returns to normal. Preserve the expected and actual result so the test becomes certification evidence rather than an informal demonstration.
Govern Test Webhooks and Event Replay
Sandbox webhook endpoints need the same subscription enterprise approval workflows, signature verification, replay protection, and tenant isolation. Use test signing keys and obvious environment markers. Production subscribers should never receive sandbox events, and sandbox endpoints should reject production signatures.
Allow controlled replay by event ID so consumers can test idempotency and recovery. Replayed events should retain the original event identity and carry delivery metadata that distinguishes replay from a new business event. This lets teams verify behavior without inventing a second approval, authorization, or order.
Make Test Evidence Machine Verifiable
| Evidence artifact | What it proves | Promotion use |
|---|---|---|
| Environment inventory | Owners, endpoints, identities and dependencies are known | Confirms isolation and accountability |
| Scenario manifest | Fixture version and expected CCA result are defined | Supports repeatable regression |
| Contract results | Requests, responses and events match the supported version | Confirms interface compatibility |
| Policy results | Eligibility, denial and approval paths behave correctly | Confirms CCA authority |
| BCM handoff results | Only valid environment-bound authorizations create test orders | Confirms ordering boundary |
| Recovery results | Retries, status queries and unknown outcomes avoid duplicates | Confirms safe resilience |
| Security results | Scopes, tenant isolation, secrets and signatures are enforced | Confirms access control |
| Promotion decision | Approver, evidence set, constraints and expiry are recorded | Authorizes production activation |
Control Configuration and Secret Promotion
Do not copy a complete sandbox configuration into production. Promote reviewed configuration intent through controlled deployment, then inject environment-specific endpoints, tenant references, secrets, signing keys, quotas and monitoring destinations. The organization should create production credentials for the approved consumer only after certification. Store secrets outside source code and test fixtures. Rotate any credential exposed during troubleshooting. Prevent logs, screenshots and exported test bundles from carrying production values. A successful certification result does not justify reusing the certification token in production.
Use a Production Readiness Gate
| Gate question | Required evidence | Decision owner |
|---|---|---|
| Is the business purpose still approved? | Current sponsor, owner, scope and tenant profile | CCA integration governance |
| Did mandatory scenarios pass? | Versioned automated results and exceptions | Certification authority |
| Is BCM handoff safe? | Authorization, idempotency and unknown-outcome results | BCM software operations |
| Are webhooks controlled? | Subscription, signature, replay and dead-letter tests | Platform and BOC operations |
| Are production controls ready? | Credentials, quotas, monitoring, support and rollback | Security and operations |
| Are residual risks accepted? | Named owner, expiry and remediation plan | Accountable risk authority |
Monitor Drift After Certification
A sandbox loses value when its contract, policy fixtures or BCM simulation drift from production. Track supported API versions, rule-package versions, event schemas, error categories and critical configuration. Publish known differences and give them owners. Do not describe an environment as production-like when important enterprise governance platform behavior is missing.
Recertify when a consumer changes identity, scopes, tenant reach, contract version, approval behavior, webhook processing, order submission, or recovery logic. Targeted tests may be enough for a low-risk change, but the decision and evidence should remain explicit.
Retire Test Environments and Data
Temporary tenants, credentials, queues, and fixtures should have expiry dates. Before deletion, identify open test approvals, simulated BCM orders, webhook deliveries, and BOC cases. Close or archive them according to policy, then revoke access and remove event routes.
Retirement should include residual-access monitoring. Calls to a retired sandbox may reveal hard-coded credentials, forgotten jobs or documentation that still directs teams to an obsolete endpoint. Remove synthetic data when its purpose ends; test status does not justify indefinite retention.
Implementation Roadmap
- Define developer, integration, certification, preproduction, and production environments with explicit purposes and authority boundaries.
- Issue separate tenants, identities, secrets, signing keys, quotas, queues, and logs for every environment.
- Create versioned synthetic scenarios covering identity, eligibility, approvals, templates, quantities, and tenant isolation.
- Maintain contract parity for APIs, errors, idempotency, and webhook envelopes while documenting capability differences.
- Disable physical fulfillment structurally and use an isolated BCM test instance or faithful simulation.
- Automate positive, negative, destructive, replay, and unknown-outcome tests with preserved evidence.
- Verify CCA decisions, BCM authorization enforcement, and BOC exception handling through stable correlations.
- Promote reviewed configuration intent while creating new environment-specific production secrets and controls.
- Use a production-readiness gate with accountable approval, residual-risk ownership, and rollback.
- Monitor parity drift, recertify material changes, and retire unused test environments cleanly.
Frequently Asked Questions
Why does a business card API need a sandbox?
It lets teams validate contracts, CCA policy outcomes, approvals, BCM handoffs, and failure recovery without exposing production identities or creating physical orders.
Can production employee data be copied into the sandbox?
Use synthetic data by default. Masked production data should require a documented purpose, approval, minimization, protection, and deletion plan.
What is BCM in the test environment?
Business Card Manager (BCM) is the business card ordering management system or software. In testing, its behavior should be isolated or simulated so valid test authorizations create test records only.
Should sandbox and production use the same credentials?
No. Each environment needs unique consumer identities, secrets, signing keys and scopes.
How can the sandbox prevent accidental printing?
Remove production provider routes, bind authorizations to the test environment and ensure BCM test orders cannot enter physical fulfillment.
What should remain consistent with production?
API contracts, policy semantics, authorization boundaries, idempotency, error categories, webhook envelopes and correlation behavior should remain consistent.
Can webhook events be replayed for testing?
Yes, under controlled replay. Keep the original event ID and mark the delivery as a replay so the consumer proves idempotent processing.
When is the integration ready for production?
When required evidence proves the approved purpose, CCA policy behavior, BCM handoff, security, event processing, recovery, monitoring, support, and rollback controls.
The Strategic Outcome
A governed sandbox converts testing from informal technical experimentation into reliable production evidence. Integration teams can explore safely, exercise failure conditions repeatedly, and prove how the consumer respects CCA decisions. Security and operations gain clear environment boundaries, while auditors can connect the promoted configuration to the results that justified activation.
The model reinforces the core purpose of the CCA website. CCA remains the enterprise authority, Business Card Manager remains the business card ordering management software, and BOC remains the oversight layer. Nonproduction accelerates integration without creating a second, weaker path to business identity execution.
Select one current business card integration and map every development, test, certification, and production dependency. Verify that identities, data, authorizations, BCM order records, webhooks, and secrets cannot cross environments. If a test path can reach physical fulfillment or a production identity, contain that risk before continuing certification.