

API Versioning and Backward Compatibility For Enterprise Business Card Integrations
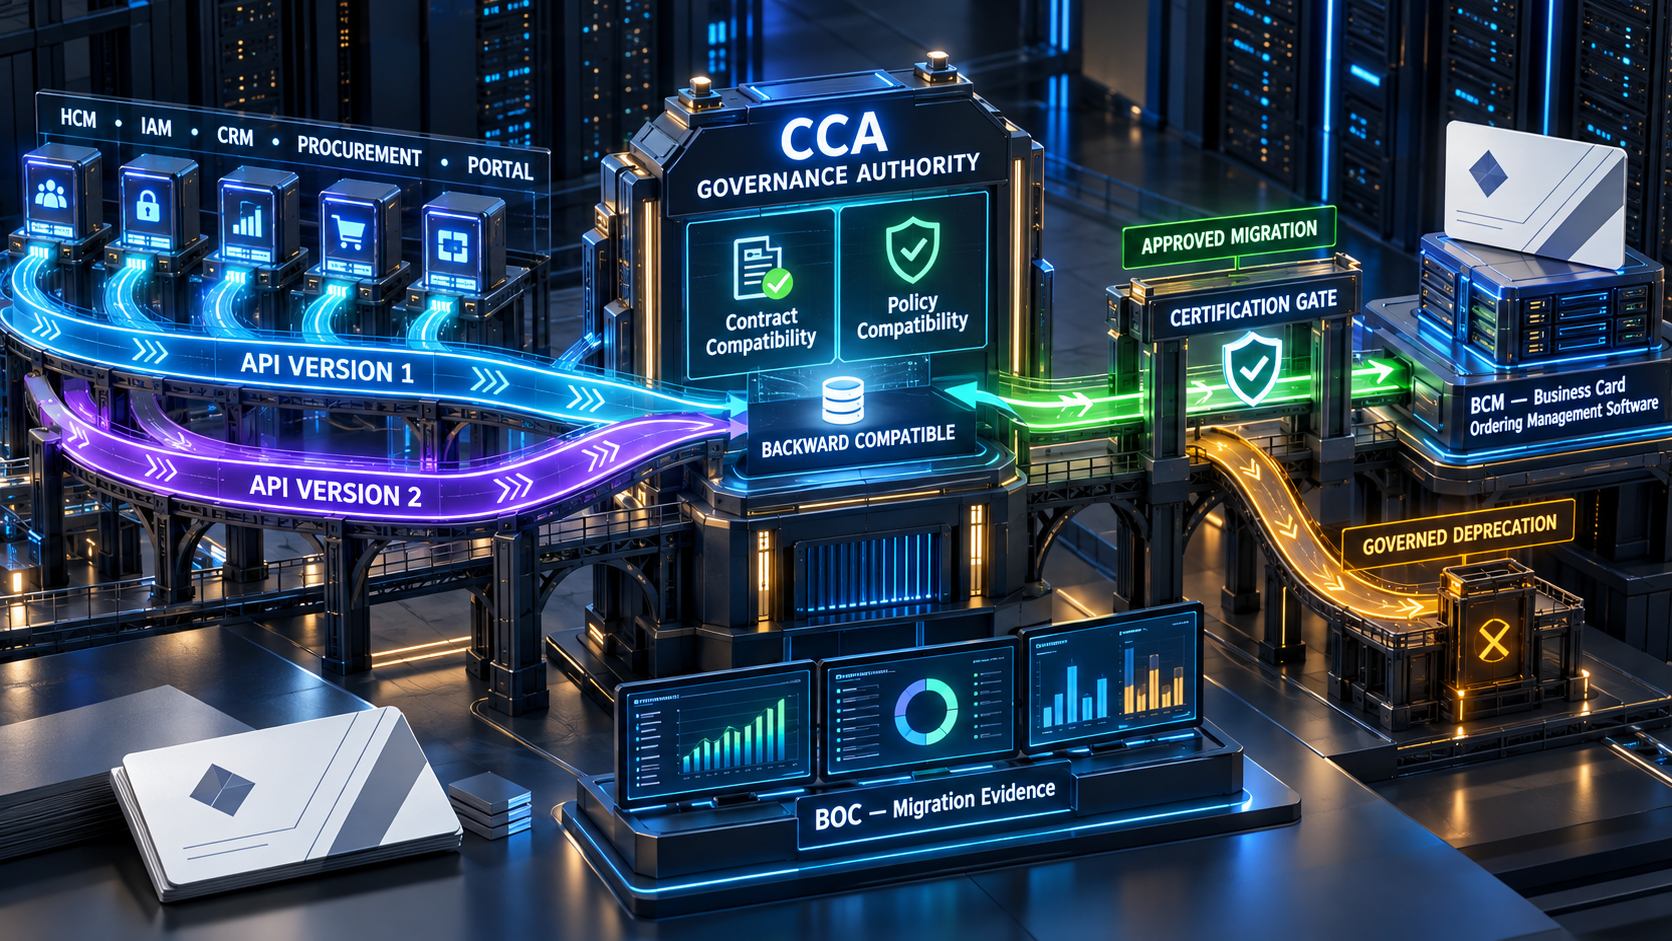
Evolving connected services without weakening governed business identity execution. Contract stability Policy continuity Controlled migration.
API Change Must Preserve the Purpose of CCA
Enterprise integrations do not remain static. HCM platforms add fields, identity providers change claims, procurement systems revise accounting structures, portals adopt new experiences, and fulfillment services introduce new status models. A business card API must evolve with those systems. The risk is not change itself; it is allowing a technical change to weaken the controls that make business identity execution trustworthy.
Color Card Administrator (CCA) is the governance and authority layer for business card eligibility, approved identity fields, templates, quantities, approval paths, and ordering rights. Business Card Manager (BCM) is the business card ordering management system or software that executes valid CCA-authorized orders. Business Ops Center (BOC) provides operational visibility, exception handling, and migration evidence. Versioning must keep these responsibilities intact across every supported contract.
Compatibility Is More Than a Payload That Still Parses
A response may remain syntactically valid while its business meaning changes. A renamed status could alter a portal decision. A new default could bypass approval. A field that becomes optional could allow incomplete card identity. A broader scope could expose another legal entity. For CCA, backward compatibility therefore has two dimensions: contract compatibility and governance compatibility.
Contract compatibility means an existing consumer can still send, receive, and validate the documented structure. Governance compatibility means the same authorized intent still produces an equivalent CCA decision and an equivalent BCM ordering boundary. Both are required. If a consumer continues running but reaches a different policy outcome without deliberate migration, the change is not safely compatible.
Classify Changes Before Release
| Change class | Example | Compatibility judgment | Required action |
|---|---|---|---|
| Additive | New optional response field | Usually compatible when consumers ignore unknown fields | Contract tests and notice |
| Clarifying | More precise documentation or error guidance | Compatible only if behavior is unchanged | Documentation review |
| Behavioral | Different approval or defaulting logic | Potentially breaking even with identical schema | New version or explicit opt-in |
| Structural | Rename, remove or change field type | Breaking for existing consumers | New major version and migration |
| Security | Narrower scopes or stronger signature rules | Necessary but operationally disruptive | Controlled security transition |
| Governance | Changed eligibility, authority or template semantics | Breaking when outcomes differ | Policy version and recertification |
Separate Contract Version from Policy Version
The API contract and the CCA policy package change for different reasons. Contract versions describe resources, fields, errors, events and interaction rules. Policy versions describe eligibility, authoritative sources, approval requirements, templates, quantities and routing decisions. Combining them into one opaque version number makes it difficult to explain why an outcome changed.
Every decision record should capture both. A consumer may remain on API version one while moving to a newly approved policy package, or it may adopt API version two while temporarily retaining an equivalent policy baseline. BOC can then compare outcomes by contract, policy and tenant rather than treating every difference as an unexplained print vendor API integration failure.
Adopt a Predictable Version Strategy
Use a version mechanism that consumers can discover and test consistently. The version may appear in the path, a media type or a required header, but it should not be inferred silently from payload shape. CCA should reject unsupported or ambiguous requests with a stable error category and direct the consumer to supported versions and migration guidance.
Major versions should represent intentionally breaking contracts. Minor, date-based or capability releases may introduce compatible additions, but their guarantees need to be explicit. Avoid creating a new major version for every small change; excessive versions increase test combinations, slow security remediation and leave policy behavior fragmented across consumers.
Define Compatibility Rules for Common API Elements
| API element | Generally safe evolution | Breaking evolution | CCA control |
|---|---|---|---|
| Request fields | Add optional field with no policy-changing default | Remove, rename, retype or newly require field | Validate by declared version |
| Response fields | Add documented optional field | Remove field or change meaning or format | Preserve decision semantics |
| Enumerations | Add value only if consumers tolerate unknowns | Rename value or reuse old value with new meaning | Publish unknown-value behavior |
| Errors | Add detail under stable category | Change category used for workflow decisions | Keep machine-readable taxonomy |
| Pagination | Add optional cursor metadata | Change ordering or cursor semantics | Protect complete retrieval |
| Webhooks | Add optional data in stable envelope | Change event identity, signature or delivery meaning | Version schema and subscriptions |
| Authorization | Add narrower optional capability | Broaden existing scope or weaken claims | Use least privilege and recertify |
Protect the CCA to BCM Authorization Boundary
BCM must never reconstruct governance from a version-specific request. CCA should issue a version-neutral authorization artifact that locks the approved order intent: tenant, program, template, governed fields, quantity, destination rules, expiry, environment, and correlation. BCM validates that artifact before creating the order. This prevents a legacy consumer from editing approved values or relying on a deprecated default.
When authorization format itself changes, support explicit validators for the permitted versions and bind each artifact to its issuer and validation rules. Do not accept an old authorization merely because its signature is valid. Expiry, scope, policy version, and revocation status remain part of the decision. BOC should record which validator accepted the handoff and which BCM software release processed it.
Version Events and Webhooks Deliberately
Event consumers are often harder to migrate than request-response clients because delivery continues asynchronously. Keep a stable envelope for event ID, tenant, event type, occurred time, schema version, and correlation. Version the event data when meaning or structure changes, and let approved subscribers select supported schemas during a controlled transition.
Never send a new incompatible shape under an old schema label. Preserve signature verification, replay protection, idempotency, and delivery evidence across versions. During dual delivery, ensure two schema representations of one business event retain the same event identity or an explicit equivalence reference so consumers do not trigger duplicate approvals or BCM orders.
Use Consumer-Driven Contract Testing
An API specification describes the provider contract, but production safety also depends on how consumers interpret it. Maintain consumer-driven tests for the fields, enumeration values, error categories, ordering guarantees, and events each integration actually uses. Run them against every candidate CCA release and every supported major version.
Contract testing should include enterprise governance platforms assertions. For a fixed synthetic scenario, the test should confirm the CCA eligibility outcome, locked identity fields, approval requirement, authorization scope, and expected BCM handoff. A test that checks only HTTP status and JSON shape can miss the change that matters most.
Create a Compatibility Test Matrix
| Test dimension | Minimum coverage | Evidence retained |
|---|---|---|
| Supported clients | Current and oldest supported consumer versions | Client version and result |
| Policy outcomes | Eligible, denied, incomplete, and approval-required scenarios | Decision and reason category |
| BCM handoff | Valid, altered, expired and repeated authorizations | Order acceptance or rejection |
| Events | Current and transition schema subscriptions | Event identity and delivery result |
| Resilience | Retries, timeouts and unknown outcomes | Idempotency and recovery proof |
| Security | Scopes, tenant isolation, signatures and revoked clients | Access-control result |
| Performance | Representative rate and payload boundaries | Latency, quota and error behavior |
Publish a Deprecation Policy Consumers Can Plan Around
Deprecation should be a managed lifecycle, not a surprise announcement. Publish the affected version, reason, replacement, migration guide, sandbox availability, support window, telemetry method, target retirement date and escalation path. State whether the deadline is a goal or a committed removal date, and explain any security condition that could shorten the window.
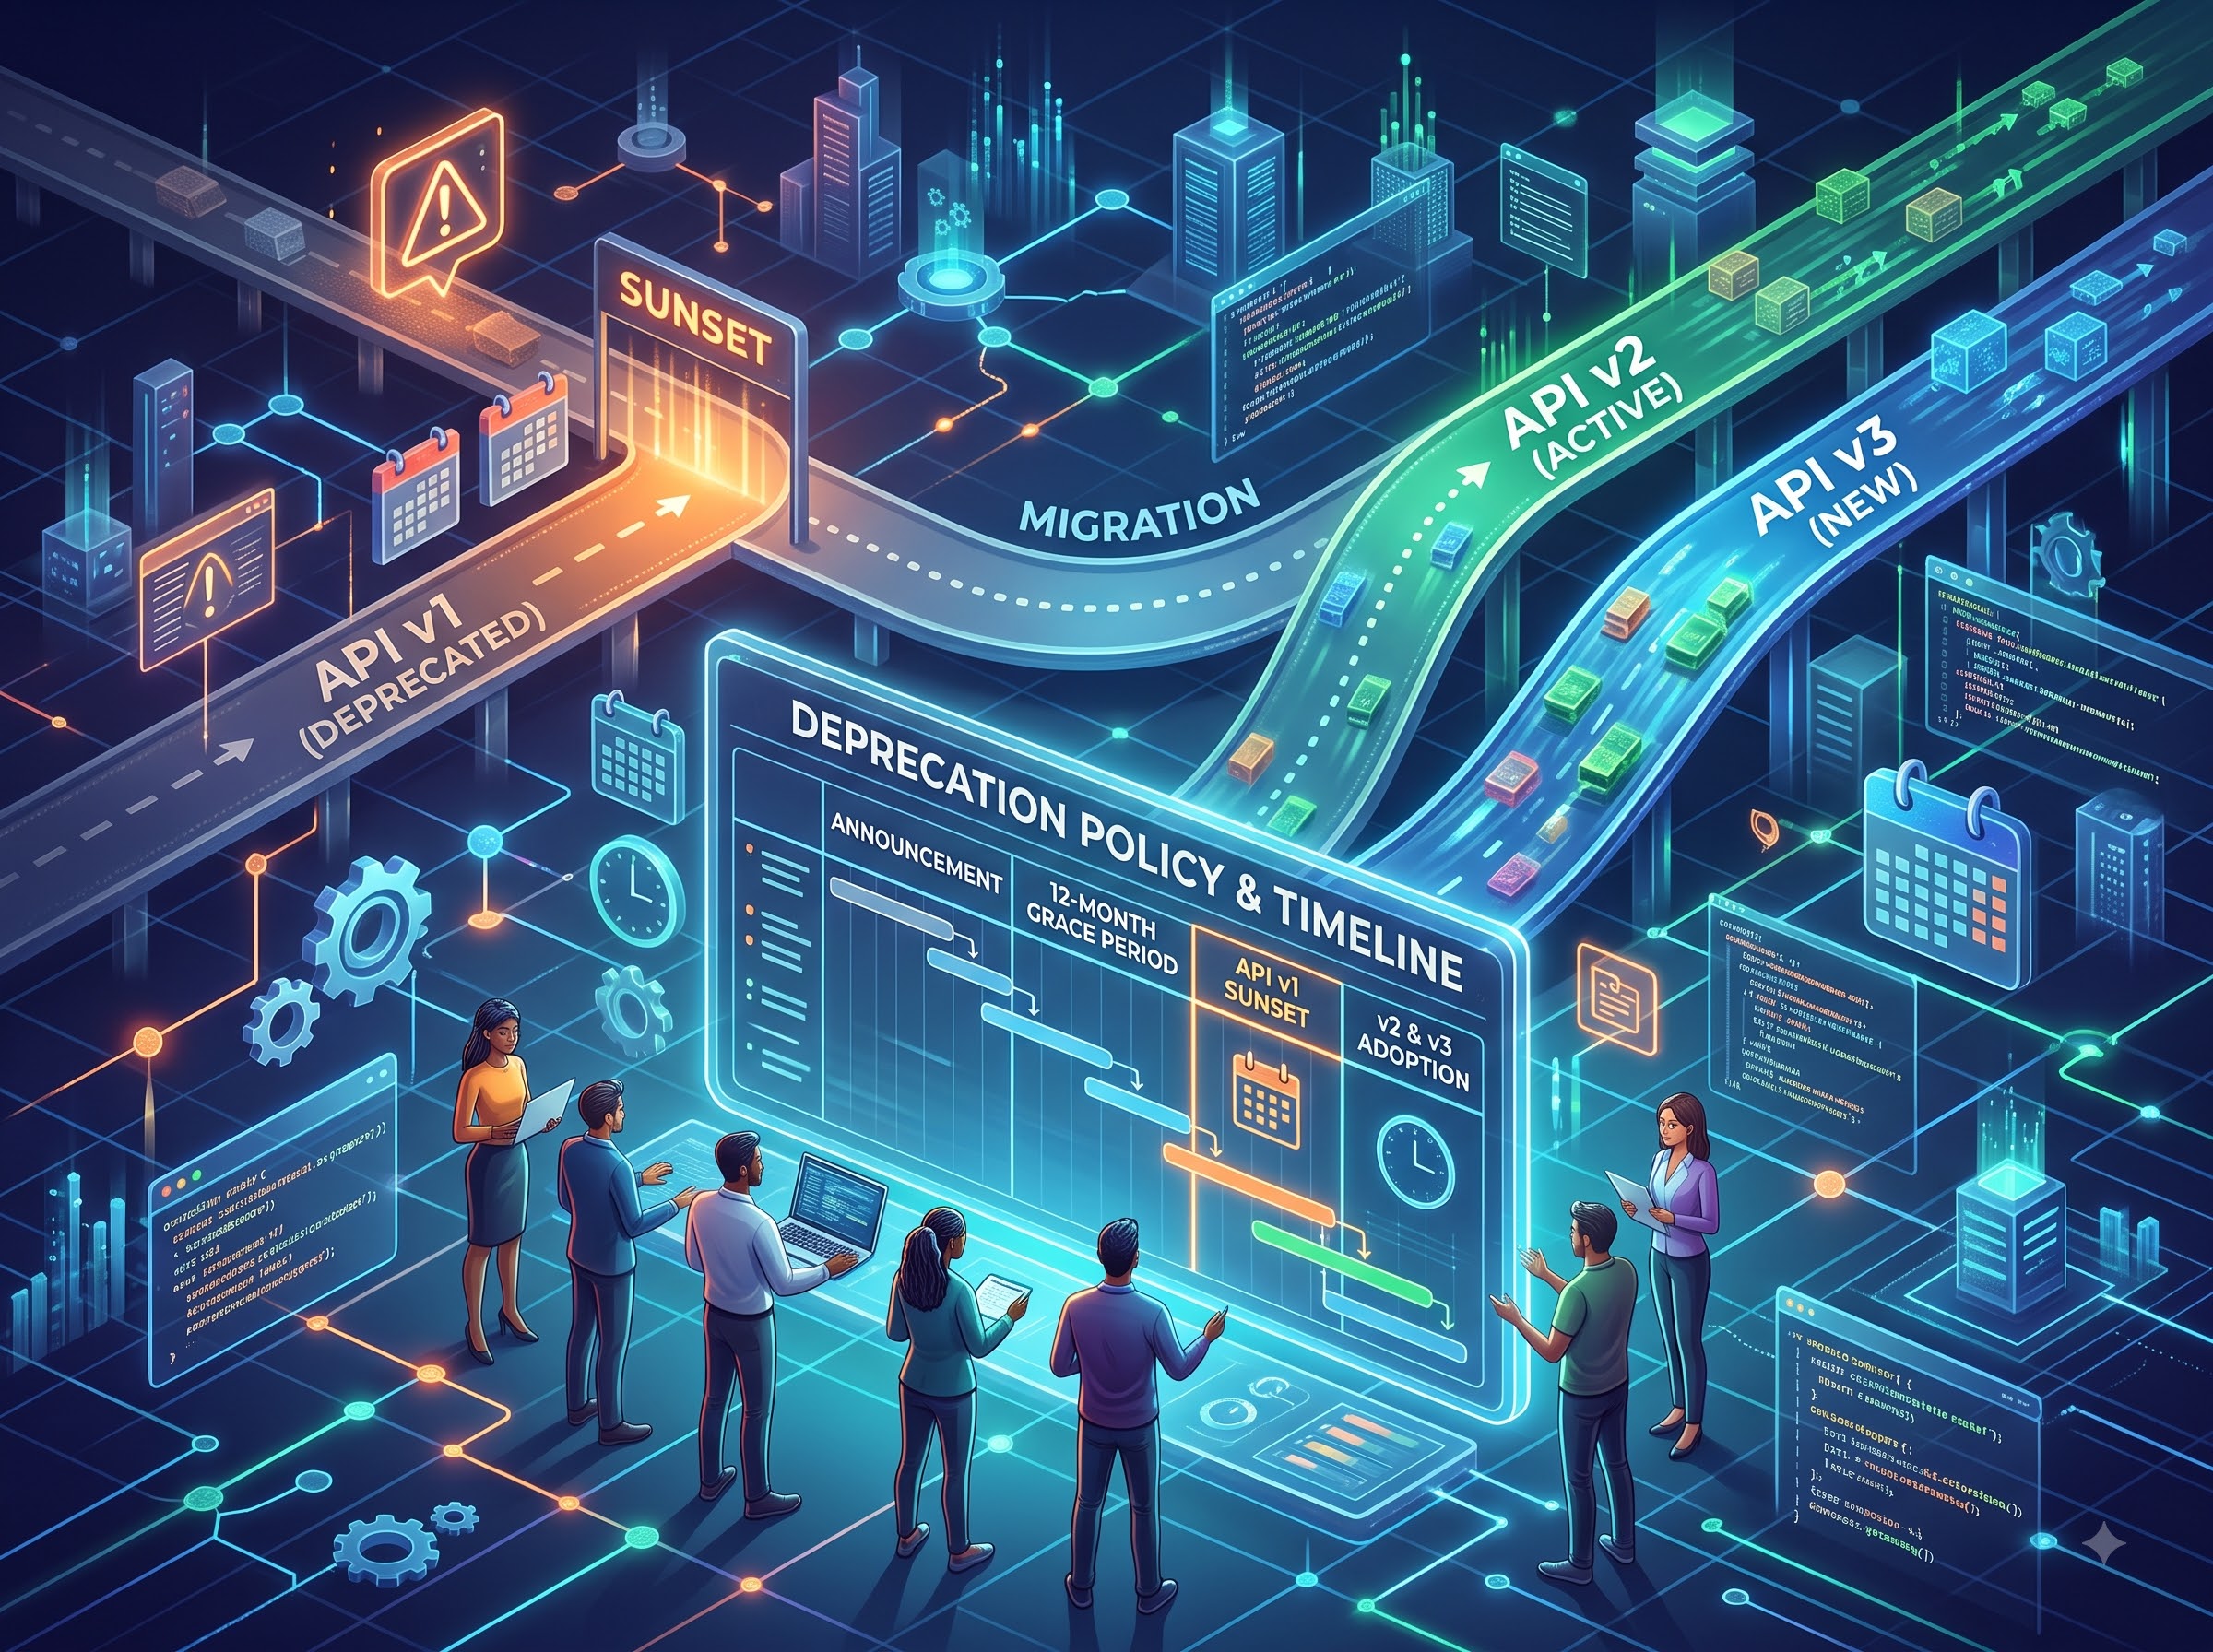
A predictable policy does not mean every version receives indefinite support. It means consumers can distinguish normal evolution from urgent remediation and budget the work. High-risk security or governance defects may require accelerated action, but CCA should still provide precise impact guidance, controlled exceptions where appropriate and visible executive ownership.
Manage Migration as an Inventory of Consumers
Version retirement begins with knowing who depends on it. Maintain a registry of consumer identity, business owner, technical owner, tenant reach, purpose, scopes, contract version, policy version, webhook schemas, last activity and certification state. Shared credentials make this difficult because traffic cannot be attributed reliably; issue distinct identities for distinct consumers.
Use runtime telemetry to validate the inventory. Track version headers, endpoints, deprecated fields and event subscriptions without logging unnecessary card identity data. BOC dashboards should show active consumers, migration stage, failed tests, exception expiry and residual traffic. A spreadsheet assembled near the retirement date is not an adequate control.
Run Old and New Versions in Parallel Without Splitting Authority
A transition may require two API versions to operate simultaneously, but there should still be one CCA authority model. Route both versions into a canonical internal decision representation, apply the approved policy package and produce equivalent authorization evidence. Version-specific adapters should translate contracts; they should not create separate eligibility logic.
Use shadow evaluation where appropriate. Process a copy of eligible non-sensitive requests through the new adapter without creating a second authorization or BCM order, then compare decisions and normalized outputs. Investigate differences by contract, data mapping, and policy. Shadow traffic must remain isolated from fulfillment and respect data-minimization rules.
Control Exceptions and Extended Support
Some consumers cannot meet the standard migration date because of regulated change windows, vendor dependencies, or critical business cycles. Treat extended support as a governed exception. Record the owner, justification, affected tenants, compensating controls, accepted risk, revised deadline, and approval. Exceptions should expire automatically rather than becoming permanent undocumented versions.
Do not let one delayed consumer prevent security improvements for everyone. Where feasible, isolate the legacy path with narrower scopes, lower quotas, stronger monitoring, and restricted functionality. Prevent new consumers from onboarding to a deprecated version after the migration window begins.
Use a Production Migration Gate
| Gate question | Required evidence | Accountable owner |
|---|---|---|
| Is the target contract approved? | Specification, change classification and security review | CCA API governance |
| Are CCA outcomes equivalent or intentionally changed? | Scenario comparison and approved policy differences | Business identity governance |
| Is the BCM boundary preserved? | Authorization, idempotency and altered-payload tests | BCM software operations |
| Are events safe? | Schema, signature, replay and dual-delivery results | Integration operations |
| Can the consumer recover? | Timeout, retry, status query and rollback tests | Consumer owner |
| Is retirement measurable? | Inventory, telemetry, communications and exception plan | Program owner |
Retire a Version Cleanly
Before retirement, confirm that active traffic, scheduled jobs, webhook subscriptions, documentation examples and credentials have moved. Freeze new registrations, issue staged warnings, and test the retirement response. After shutdown, return a stable machine-readable error that identifies the retired version and supported destination; do not silently route requests to a new contract.
Revoke version-specific credentials and subscriptions that no longer serve another approved purpose. Preserve the decision record, migration evidence and required audit history, while applying retention limits to operational payloads. Monitor residual calls because they can reveal forgotten batch jobs, hard-coded endpoints or unauthorized reuse.
Implementation Roadmap
- Inventory every API and webhook consumer, its owner, purpose, scopes, tenants, versions and current activity.
- Define compatibility rules for request fields, responses, enumerations, errors, pagination, events and authorization.
- Separate contract versions from CCA policy versions and record both on every decision and handoff.
- Create canonical internal decision and authorization models so adapters cannot fragment governance.
- Build synthetic consumer-driven tests that verify contract shape and CCA policy outcomes.
- Validate BCM acceptance, rejection, idempotency, and unknown-outcome recovery for every supported major version.
- Publish lifecycle stages, support windows, migration guides, sandbox access and retirement criteria.
- Run parallel and shadow validation without issuing duplicate authorizations or physical orders.
- Govern extended support with named risk owners, compensating controls and automatic expiry.
- Retire credentials, subscriptions and documentation only after telemetry confirms migration completion.
Frequently Asked Questions
Why does a business card API need versioning?
Versioning lets CCA evolve interfaces while consumers understand which contract and behavior they can rely on. It creates a controlled migration path when a change cannot remain compatible.
What does backward compatibility mean for CCA?
Existing consumers must continue to understand the contract, and equivalent authorized intent must retain equivalent governance outcomes unless an approved migration explicitly changes them.
Is adding a response field always safe?
Usually only when it is optional, documented, and consumers are required to tolerate unknown fields. If the new field changes decisions or interpretation, additional controls are needed.
What is BCM in this architecture?
Business Card Manager (BCM) is the business card ordering management system or software. It accepts only valid CCA-authorized order intent and manages the ordering workflow.
Should every policy change create a new API version?
No. Track policy version separately. Create a new API version when the external contract or observable semantics break compatibility.
How should webhook schemas be changed?
Keep a stable event envelope, declare the schema version, support a controlled transition, and preserve event identity so alternate representations do not create duplicate actions.
How long should an old version remain available?
Use a published support policy based on consumer impact, security risk, and enterprise change cycles. Avoid both surprise retirement and indefinitely unsupported versions.
Can CCA automatically move consumers to a new major version?
No. Major-version migration should be explicit, tested, and approved. Silent routing can change business meaning and hide incompatibility.
How does BOC support migration?
BOC provides consumer inventory, telemetry, exception tracking, readiness evidence, and residual-traffic monitoring across the transition.
When is migration complete?
When approved consumers pass certification, BCM and event controls are proven, production telemetry shows the target version, exceptions are closed or governed, and the old path can be retired safely.
The Strategic Outcome
Governed versioning lets enterprises modernize integrations without trading control for speed. Teams can introduce useful capabilities, respond to security needs, and support new enterprise systems while preserving stable contracts for current consumers. Decision evidence explains whether a difference came from the interface, the policy package, the consumer or BCM execution.
The approach reinforces the core purpose of the CCA website. CCA remains the enterprise authority for business card management and ordering rights. Business Card Manager remains the business card ordering management software that executes authorized intent. BOC makes migration status, exceptions, and operational outcomes visible. Versions change; authority does not become ambiguous.
Choose the oldest active business card API version and identify every consumer, owner, tenant, scope, policy package, and webhook subscription that depends on it. Compare its behavior with the target version using synthetic governance scenarios. If equivalent intent produces unexplained differences in CCA decisions or BCM ordering behavior, resolve those differences before scheduling migration.