

Configuration Drift Detection and Remediation for Enterprise Business Card API Integrations
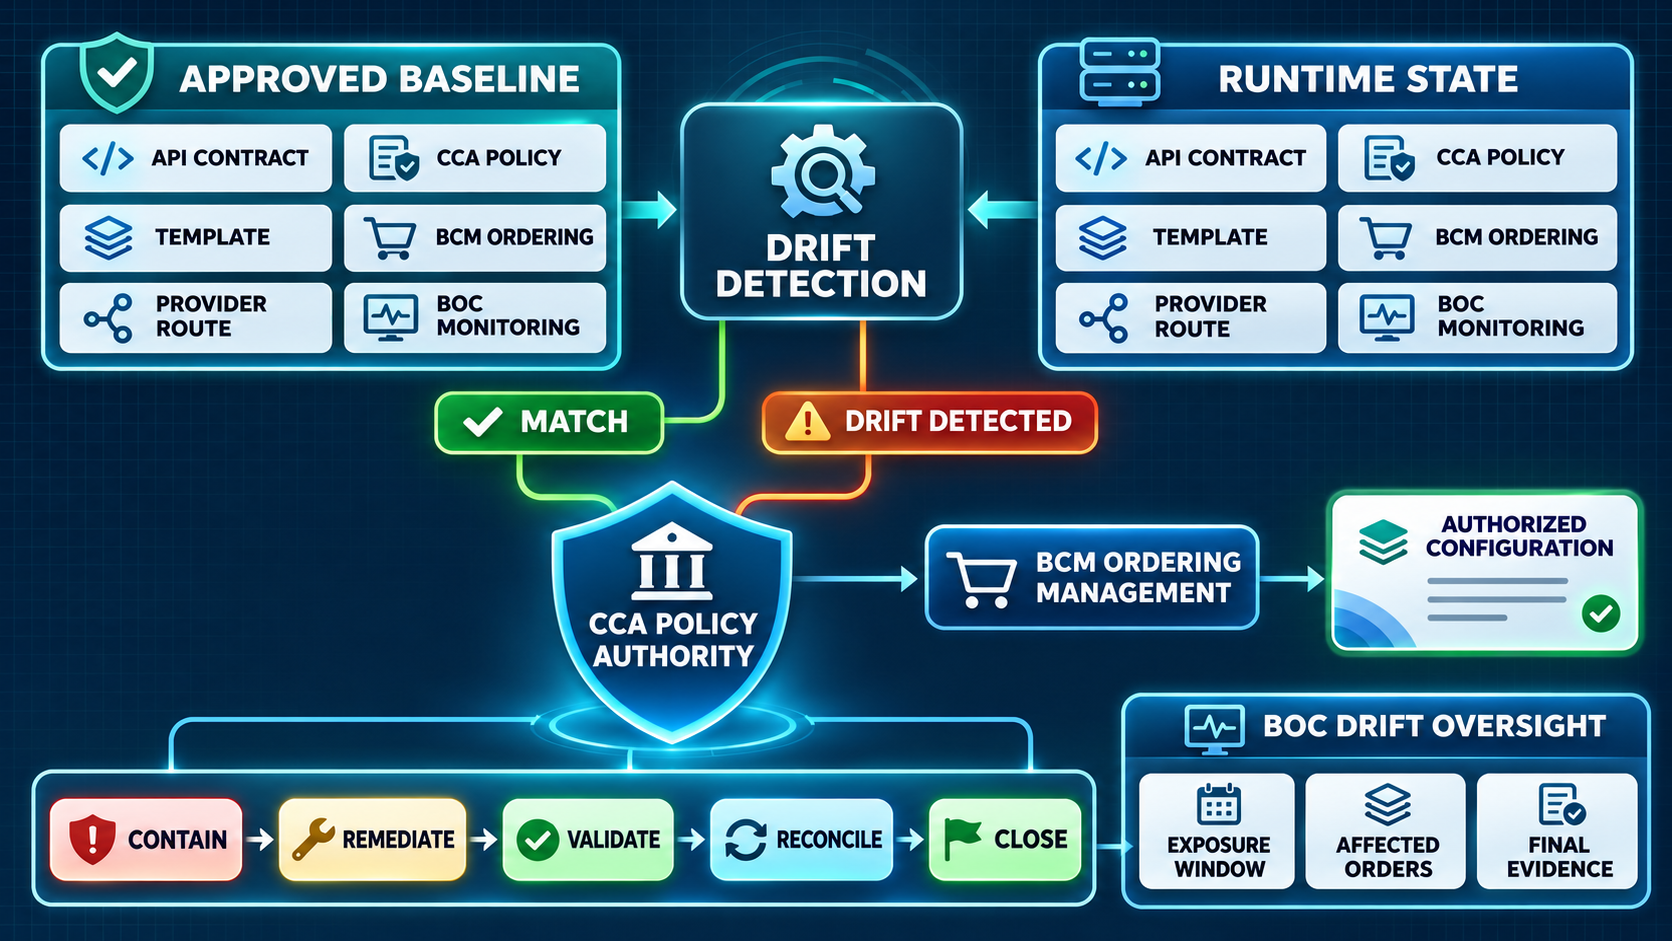
Keeping API contracts, CCA policy, BCM ordering, and operational evidence aligned with approved state.
Configuration Drift Changes Business Outcomes
Enterprise integrations rarely fail only because code is broken. A field mapping can change in one environment, an API gateway can point to a different route, a CCA policy package can be older than expected, a BCM template can be edited outside the release process or a provider credential can reference the wrong account. Each component may remain available while the complete business card decision behaves differently from the approved design.
Configuration drift is the difference between an approved baseline and the state actually running. Drift can be authorized, accidental or malicious. Governance requires the enterprise to know which configuration controls identity, eligibility, templates, approvals, quantities, ordering, fulfillment and evidence; detect differences quickly; assess business impact; and restore or approve the correct state.
Keep CCA, BCM, and BOC Responsibilities Explicit
Color Card Administrator, or CCA, is the enterprise policy and orchestration authority for API-connected business card programs. CCA determines eligibility, approved identity, templates, quantities, approvals and provider routing. The approved CCA policy and decision configuration should be versioned, promoted and reconciled as controlled enterprise state.
Business Card Manager, or BCM, is the business card ordering management system or software. BCM manages permissions, approvals, templates, quantities, authorized orders, proofing, production coordination, delivery status and reporting. BCM configuration should execute CCA-authorized intent without introducing an alternate eligibility rule, unmanaged template or unauthorized route.
Business Ops Center, or BOC, provides drift visibility, exception ownership and reconciliation. BOC correlates approved baselines, detected differences, affected decisions, BCM orders and final remediation. CCA owns authority, BCM owns governed execution and BOC owns operational accountability.
Build a Configuration Inventory
| Configuration domain | Examples | Business risk |
|---|---|---|
| API access | Endpoints, scopes, certificates and workload identity | Wrong system or privilege boundary |
| Contracts | Schema, required fields, enums and versions | Silent mapping or validation change |
| CCA policy | Eligibility, field authority, approvals and quantity | Unauthorized or inconsistent decision |
| Templates | Layout, brand, legal text and product mapping | Incorrect public identity or compliance text |
| BCM ordering | Permissions, workflow, proof and order state | Bypass or duplicate execution |
| Provider route | Printer, region, product and fulfillment account | Wrong production or data destination |
| BOC operations | Alerts, thresholds, owners and reconciliation | Failure remains invisible or unresolved |
Inventory must include runtime configuration, not only source files. Environment variables, feature flags, secrets references, gateway rules, queues, provider consoles and administrative edits can change behavior without modifying the application repository.
Define the Approved Baseline
A baseline is a versioned representation of approved configuration for a specific environment, card program and effective period. It should identify the owner, release, source of truth, approval evidence and expected fingerprint. The baseline must be precise enough to compare with runtime state but should not expose secret values.
Not every difference is drift. Emergency changes and approved regional variations can be valid when documented and time-bound. The baseline should support declared overlays while making unapproved deviations visible. A generic statement that production should match staging is not sufficient when the environments intentionally differ.
Classify Baseline Elements
| Element class | Example | Comparison method |
|---|---|---|
| Exact | Policy version, endpoint host or template ID | Exact value or cryptographic digest |
| Set | Approved scopes, fields or providers | Set equality and prohibited additions |
| Range | Timeout, retry or quantity threshold | Approved minimum and maximum |
| Relationship | Template belongs to program and provider route | Referential and compatibility check |
| Presence | Required alert, owner or retention rule | Exists and is enabled |
| Secret reference | Credential identifier and rotation metadata | Reference and status, never secret value |
| Effective state | Policy or template scheduled for a date | Version plus effective period |
Detect Drift Continuously
Deployment checks catch differences at release time, but drift can appear later through administrative edits, credential rotation, provider changes or failed promotion. Use event-driven detection where platforms expose configuration change events and scheduled comparison where they do not. Critical policy, route and permission changes should be evaluated quickly.
Detection should collect a normalized snapshot, compare it with the correct baseline and emit a stable drift record. Avoid storing full secrets or unnecessary identity data. The record should identify the environment, domain, object, expected state, observed state category, first seen time, owner and business impact.
Assign Drift Severity by Business Effect
| Severity | Example | Required response |
|---|---|---|
| Critical | CCA authorization bypass or production routed to unapproved provider | Contain immediately and investigate |
| High | Template, legal text, permission or field authority differs | Pause affected new orders |
| Medium | Timeout, alert or noncritical mapping outside baseline | Remediate within service target |
| Low | Metadata or display preference differs without control effect | Track and correct in normal release |
| Expected | Approved time-bound overlay or staged rollout | Monitor expiry and reconcile |
Severity should reflect authorization, identity, financial, privacy, brand and production impact. A one-character difference in an endpoint may be more serious than a large visual difference in a nonproduction dashboard.
Distinguish Drift from Version Change
A planned version change updates the approved baseline through review, testing and promotion. Drift appears when actual state differs without that governed transition or when an approved release is incomplete. Treating every difference as a release creates alert fatigue; treating every release as authorized hides failed promotion.
The drift record should link the change request, deployment, approver and effective time when available. If no approved evidence exists, classify the difference as unplanned until proven otherwise. Operators should not close drift merely because the current state appears useful.
Protect CCA Policy Integrity
CCA policy controls who is eligible, which identity can appear, what template and quantity are permitted and which approvals and routes apply. Store policy packages as versioned artifacts with review, automated tests and environment promotion. Runtime decisions should record the policy and template versions used.
Compare active policy, dependencies, field-authority mappings, effective dates and feature flags with the baseline. When critical drift exists, CCA should contain affected decisions or use the last approved policy only when rollback is safe and explicit. Silent continuation with an unknown rule set undermines the authority engine.
Verify CCA Decision Drift
| Assertion | Approved expectation | Drift signal |
|---|---|---|
| Eligibility | Controlled facts produce declared allow or deny | Decision outcome changes |
| Field authority | Each published field uses approved source | Different source wins conflict |
| Template | Program resolves approved template version | Unknown or retired template selected |
| Approval | Exception follows required route | Approval skipped or misrouted |
| Quantity | Policy limit is enforced | Order exceeds approved threshold |
| Provider route | Decision selects approved region and provider | Unapproved destination returned |
| Evidence | Decision contains versioned reason and correlation | Required evidence absent |
Protect BCM Ordering Configuration
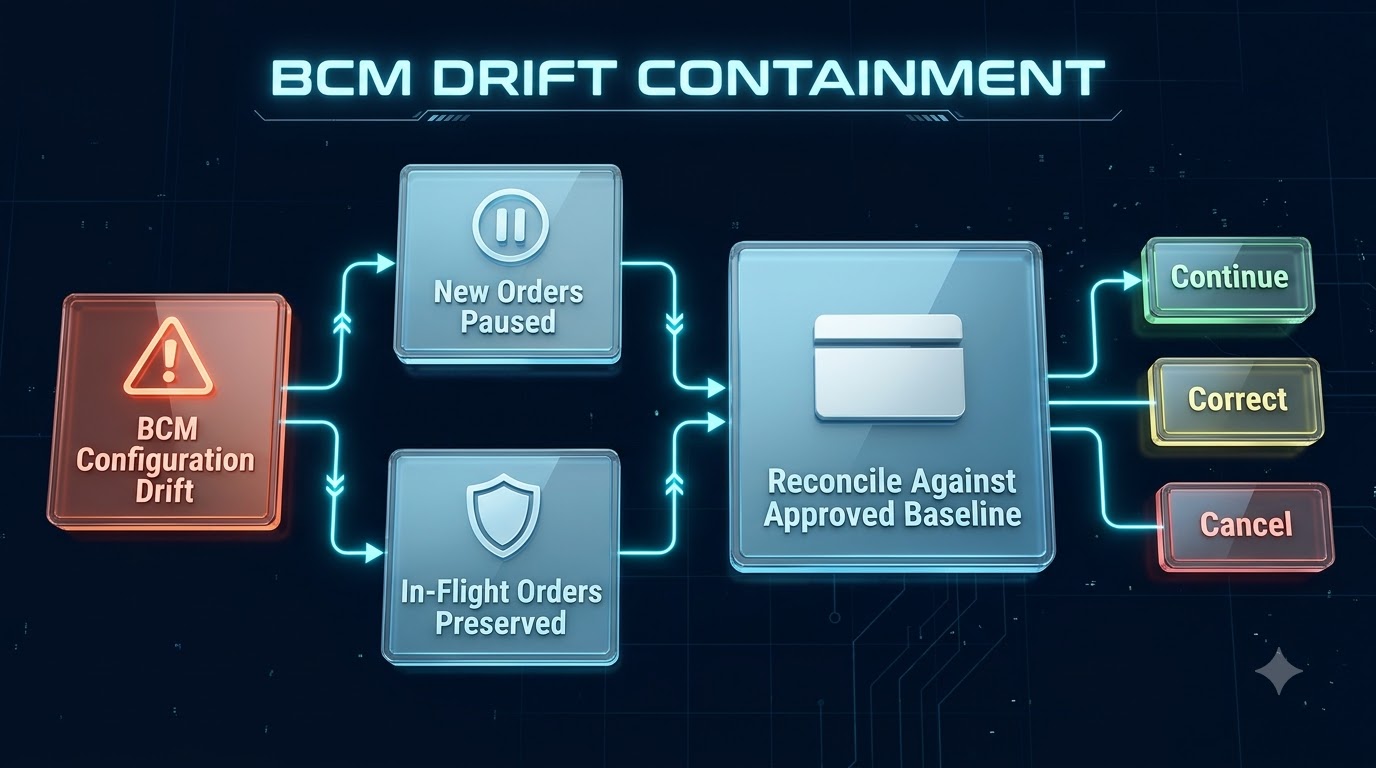
BCM should receive a locked CCA authorization and manage the approved business card order. Compare BCM permissions, workflow states, template bindings, quantity handling, proof controls, provider routing and idempotency behavior with the approved baseline. Administrative convenience should not create a second policy layer.
If BCM drift could alter identity, quantity, template, approval or route, pause affected new execution while preserving confirmed in-flight orders. Reconcile existing orders to determine whether they were created under the approved configuration before deciding on cancellation, correction or continued fulfillment.
Control Template and Provider Drift
| Drift area | Potential effect | Governed control |
|---|---|---|
| Template content | Wrong brand or legal statement | Versioned asset digest and approval |
| Product mapping | Incorrect stock, size or finish | Compatibility baseline and preflight |
| Provider account | Order reaches wrong production tenant | Approved account and credential reference |
| Regional route | Data or fulfillment crosses boundary | CCA route policy and location check |
| Shipping service | Cost or delivery commitment changes | Approved service-level mapping |
| Callback endpoint | Status evidence is lost or misdirected | Authenticated destination baseline |
Use Synthetic Monitoring to Detect Behavioral Drift
Static comparison can prove that values match, but it may miss hidden defaults, platform behavior or incomplete promotion. Synthetic transactions can test whether controlled facts still produce the expected CCA decision, BCM acknowledgment and BOC evidence. Behavioral assertions complement configuration snapshots.
Use non-personal test identities and suppressed production routes. When a synthetic outcome changes, link it to recent configuration differences before assuming an application defect. A green synthetic journey does not excuse unknown drift, but it helps prioritize changes that affect real behavior.
Contain Drift Without Creating More Drift
Containment may include disabling an affected route, pausing new authorization, forcing a circuit open or reverting to a known approved artifact. The response itself should be approved, recorded and time-bound. An operator should not patch several consoles manually without creating a new baseline or change record.
Preserve current evidence before rollback. Capture normalized differences, affected versions and transaction scope. Then use the governed deployment path to restore the approved state. Emergency correction should be reconciled into source control and the baseline so the next release does not reintroduce the defect.
Run a Controlled Drift Lifecycle
| State | Control objective | Exit condition |
|---|---|---|
| Detected | Record actual difference once | Expected and observed states captured |
| Classified | Determine severity and business scope | Owner and response target assigned |
| Contained | Stop unsafe new decisions or execution | Impact no longer expanding |
| Investigating | Find change source and affected transactions | Root condition understood |
| Remediating | Restore or approve configuration through release path | Target state deployed |
| Validating | Compare state and run behavioral assertions | Baseline and journey pass |
| Reconciling | Review CCA decisions and BCM orders during exposure | Every affected item has disposition |
| Closed | Preserve evidence and prevention action | BOC confirms completion |
Reconcile Transactions Created During Drift
Restoring configuration does not resolve orders already affected. Identify the time window, programs, decisions, templates, users and provider routes exposed to the difference. Compare source facts, CCA decision evidence, BCM order state and fulfillment outcome.
Some transactions may remain valid, while others require correction, cancellation, reauthorization or customer communication. BOC should track disposition without duplicating orders. The final record should show which configuration was active and why the chosen remedy was appropriate.
Secure Administrative Configuration Paths
Configuration interfaces can alter enterprise ordering authority. Use least privilege, strong authentication, separation of duties and time-bound emergency access. Record administrative changes with actor, object, before and after category, reason and approval reference.
Restrict direct production edits where possible. Prefer versioned configuration promoted through automation. When a platform requires console changes, capture them immediately into the approved source of truth and verify that monitoring observes the resulting state.
Use BOC for Drift Operations
| BOC signal | Operational question | Action |
|---|---|---|
| New drift | Which object differs from which baseline? | Assign domain owner and severity |
| Exposure window | When did the difference begin? | Identify affected decisions and orders |
| Repeated drift | Is automation or ownership failing? | Open systemic problem review |
| Baseline expiry | Is an approved overlay still valid? | Remove, extend through approval or escalate |
| Behavior change | Did a synthetic or production outcome shift? | Correlate configuration and decision versions |
| Remediation status | Was the approved state restored everywhere? | Verify runtime and release source |
| Reconciliation gap | Do affected orders lack final disposition? | Recover evidence before closure |
Measure Configuration Governance
| Measure | What it reveals | Target direction |
|---|---|---|
| Baseline coverage | Critical configuration has an approved reference | Complete |
| Time to detect | Drift remains active before visibility | Decrease |
| Time to contain | Unsafe impact continues after detection | Decrease |
| Unauthorized drift | Difference lacks approved change evidence | Zero |
| Repeat drift rate | Root cause or release process remains weak | Decrease to zero |
| Affected order count | Business exposure from configuration difference | Decrease |
| Reconciliation coverage | Every exposed transaction has disposition | Complete |
Implement Drift Governance in Stages
- Inventory API, identity, CCA, template, BCM, provider and BOC configuration domains.
- Assign an owner, source of truth, baseline format and effective period to each domain.
- Classify exact, set, range, relationship, presence and secret-reference comparisons.
- Automate runtime snapshots and event-driven detection without exposing secrets.
- Define severity from authorization, identity, brand, privacy and production impact.
- Contain critical drift through approved pause, route isolation or rollback controls.
- Add synthetic assertions for CCA decisions, BCM handoff and evidence behavior.
- Configure BOC ownership, service targets, exposure analysis and reconciliation.
- Test incomplete promotion, manual edit, expired overlay and provider-route drift.
- Review baselines whenever APIs, policies, templates, platforms or providers change.
Frequently Asked Questions
What is configuration drift?
It is the difference between approved configuration and the state actually running in an environment.
Why does drift matter for business cards?
It can change identity, eligibility, template, approval, quantity, provider routing or evidence while every service remains available.
What is CCA?
CCA is the enterprise policy and orchestration authority for governed business card identity, eligibility, templates, quantities, approvals and routing.
What is BCM?
BCM is the business card ordering management system or software that executes authorized orders, proofing, production coordination, delivery and reporting.
What is BOC?
BOC provides drift visibility, exception ownership, exposure analysis and source-to-card reconciliation.
Is every difference unauthorized drift?
No. Approved regional variation, staged rollout and emergency overlays can be valid when versioned and time-bound.
Can source control alone detect drift?
No. Runtime state, console edits, secrets references, gateways and provider systems also require comparison.
How should critical drift be contained?
Pause affected new decisions or execution, isolate the route or restore a known approved artifact through controlled action.
Why use synthetic monitoring with drift detection?
It shows whether a configuration difference changes the governed business outcome.
What happens to orders created during drift?
BOC should identify the exposure window and reconcile each CCA decision, BCM order and fulfillment outcome.
The Strategic Outcome
Configuration drift governance keeps the business card integration operating from approved enterprise state. CCA policy remains authoritative, BCM ordering remains aligned with authorized intent and BOC makes differences, exposure and remediation visible.
The organization gains faster detection and safer change without allowing hidden console edits, incomplete promotion or provider misconfiguration to redefine business identity execution.
Choose one production card program and compare its approved API contract, CCA policy, template, BCM workflow, provider route and BOC alert configuration with runtime state. Classify every difference, contain any authorization-impacting drift and reconcile orders created during the exposure window.