

API Consumer Onboarding and Certification For Enterprise Business Card Ordering
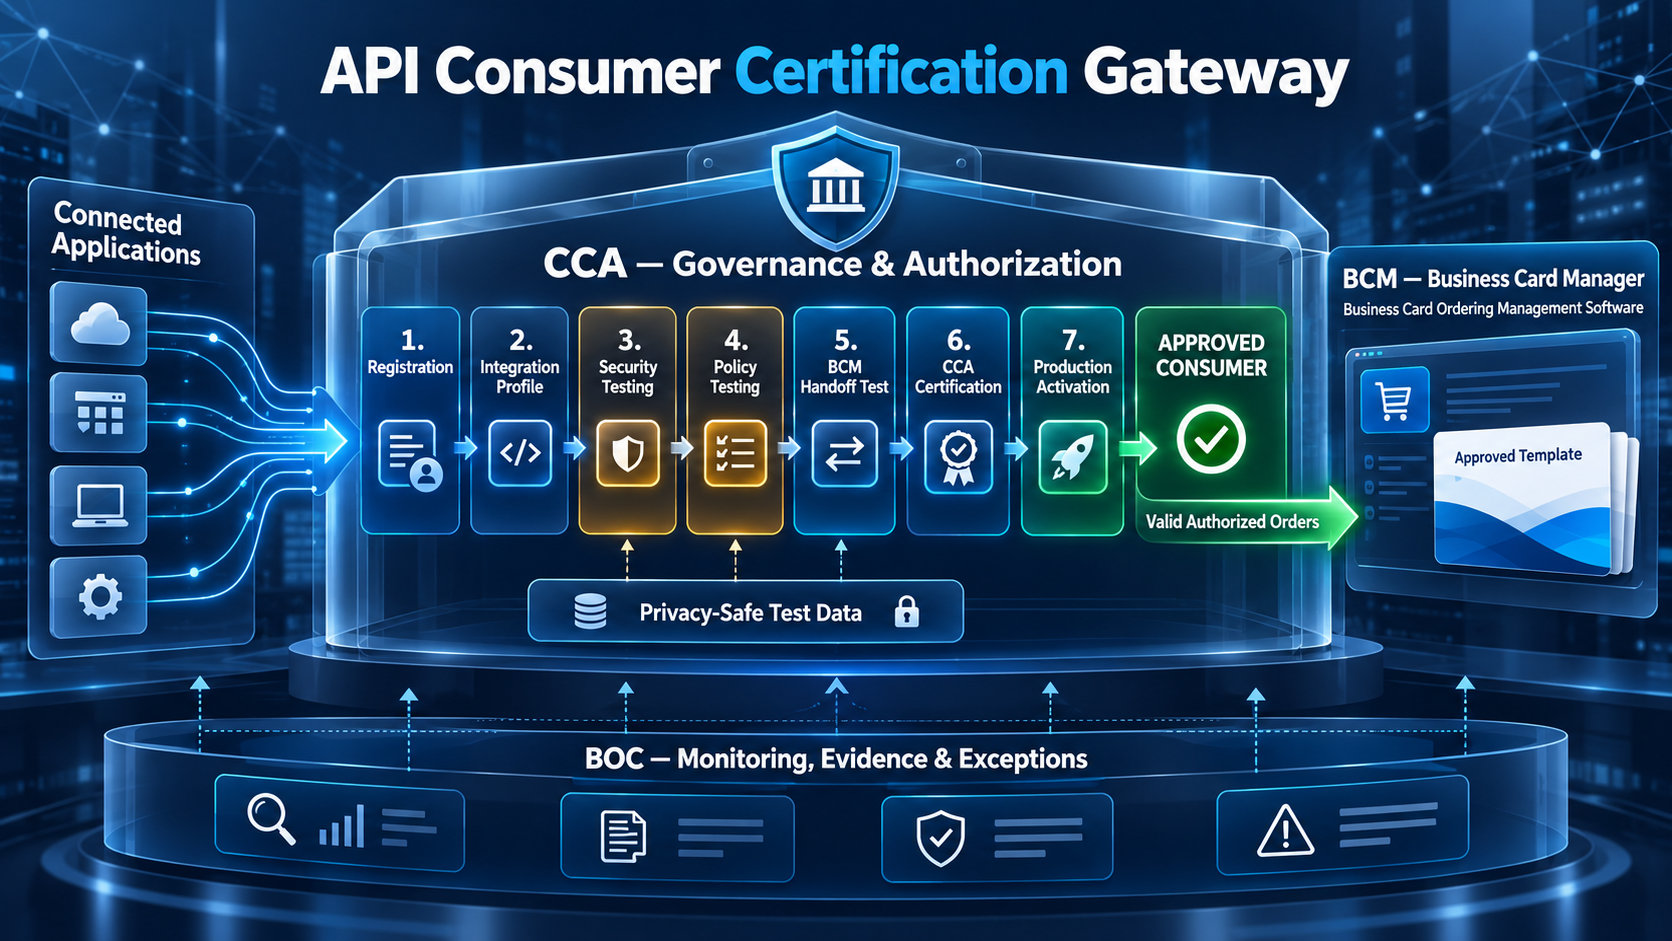
Authorizing connected applications before they initiate governed card activity. Approve, test, certify, activate, monitor, retire.
Every Connected Application Becomes a Governance Participant
An employee portal, HCM workflow, procurement application, or custom enterprise service can initiate business card activity at scale. Once connected, it can present identity context, request a policy decision, display approval state, and submit authorized work. A poorly governed consumer can also duplicate requests, expose sensitive values, misread denials, or create operational pressure. API access therefore requires more than credentials.
Color Card Administrator (CCA) should approve the use case, establish the consumer identity, constrain its permissions, and certify its behavior before production activation. CCA remains the authority for eligibility, identity fields, templates, approvals, quantities, destinations, and ordering rights. Business Card Manager (BCM) is the business card ordering management system or software that manages valid CCA-authorized orders; it is not the external print vendor. Business Ops Center (BOC) provides operational oversight, exception ownership, and reconciliation.
Treat Onboarding as a Controlled Lifecycle
| Lifecycle stage | Purpose | Required outcome | Decision owner |
|---|---|---|---|
| Register | Establish who owns the application and why it needs access | Approved business purpose and accountable owner | CCA integration governance |
| Design | Define scopes, data, flows, limits and evidence | Reviewed integration profile and test plan | Architecture, security and CCA |
| Test | Prove contract, identity, policy and failure behavior | Repeatable evidence from controlled environment | Consumer team and CCA platform |
| Certify | Evaluate readiness against mandatory controls | Pass, conditional pass or remediation required | Certification authority |
| Activate | Issue production access under approved constraints | Time-stamped production authorization | CCA access governance |
| Operate | Monitor quality, volume, errors and ownership | Healthy consumer with current certification | Consumer owner, CCA and BOC |
| Retire | Remove access and reconcile outstanding activity | Credentials revoked and records retained | Access owner and program governance |
Register the Business Purpose and Owner
Every consumer needs a human accountable owner, technical owner, business sponsor, support contact, and retirement authority. The registration should name the intended users, enterprise tenants, environments, card programs, operations, and expected volume. A generic label such as portal integration is not enough to decide whether the requested access is appropriate.
The business purpose should explain what the application will do and what it will not do. For example, a self-service portal may request CCA eligibility, show governed fields, and submit a valid authorization to BCM. It should not invent card values, select an unapproved template, bypass approval, or send a physical order directly to a provider.
Build an Integration Profile Before Credentials
| Profile element | Question to answer | Governance use |
|---|---|---|
| Consumer identity | Which application and environment is calling? | Bind credentials, logs, quotas, and ownership |
| Tenant scope | Which enterprise entities can it access? | Enforce isolation and prevent cross-tenant access |
| Operations | Which API capabilities are required? | Grant least privilege by method and resource |
| Data fields | Which identity and organizational attributes are needed? | Apply minimization and source authority |
| Volume profile | What are expected steady, peak and campaign rates? | Set quotas, bursts and capacity plan |
| User experience | How are approval, denial, delay and error shown? | Prevent misleading or unsafe actions |
| Support path | Who responds to consumer defects and incidents? | Route evidence and escalation |
| Retirement trigger | What ends the integration need? | Ensure access does not remain indefinitely |
Issue Identity and Scope With Least Privilege
Consumer credentials should be unique by application and environment. Development, test and production identities must not be interchangeable. Permissions should be explicit for evaluation, approval status, authorized submission, order status and administrative functions. A consumer that only displays status should not receive order-creation authority.
Scopes alone are not business authorization. They permit the application to request a capability; CCA still determines whether a specific employee, card program, template, quantity or destination is allowed. This distinction prevents a technically privileged integration business card governance from manufacturing a governed outcome.
Use Safe Representative Test Data
Certification needs realistic combinations of roles, locations, programs, approval routes and error states. It does not need real employee identities. Use synthetic or approved masked records that preserve the rules being tested without exposing production names, phone numbers, email addresses or complete card payloads.
Test fixtures should include eligible and ineligible identities, missing source data, conflicting fields, inactive templates, quantity limits, approval requirements, expired authorization and tenant boundaries. Each fixture needs an expected CCA decision so automated tests can detect drift.
Certify More Than the Happy Path
| Test family | Evidence required | Unsafe behavior to reject |
|---|---|---|
| Authentication and scope | Approved identity succeeds and prohibited identity fails | Shared credentials or silent scope escalation |
| Contract validation | Supported version and fields pass; invalid requests receive precise errors | Generic retry of unchanged invalid request |
| CCA policy outcomes | Eligible, denied and approval-required results display correctly | Treating denial or pending approval as outage |
| Idempotency | Repeated same intent returns the original governed result | Creating another BCM order for the same intent |
| Capacity handling | Consumer respects timing, jitter and retry budget | Immediate synchronized retry storm |
| Unknown outcome | Consumer queries status before any resubmission | Blindly creating a replacement order |
| Privacy | Logs and screens contain only permitted detail | Personal payloads in telemetry or support messages |
| Tenant isolation | Cross-tenant identifiers are rejected and recorded | Data visibility outside approved tenant |
Validate the BCM Ordering Management Handoff
Certification should prove the boundary between authority and execution. CCA issues a valid locked authorization with approved identity fields, template, quantity, destination, expiry, and correlations. Business Card Manager (BCM), the business card ordering management software, accepts that authorization once, creates the managed order, and returns a stable order identifier.
The consumer should not choose a print vendor, alter the locked payload after CCA approval, or call provider production directly. BCM software coordinates the order-management lifecycle and can exchange status with fulfillment providers. Provider events return through the governed integration so BCM and BOC can preserve evidence and reconciliation.
Test Approval and User Experience States
A consumer interface participates in the enterprise governance platform because its wording influences user behavior. Certification should inspect how it presents approval required, pending, rejected, expired, policy denied, temporarily constrained, and unknown outcome. Every state should answer whether an order exists and what action is permitted next.
Buttons and workflows matter as much as messages. Disable duplicate submission while approval is pending or order acceptance is unknown. Do not offer a manual-order alternative that leaves CCA. Display a safe correlation reference for support without exposing internal security rules.
Require Machine Verifiable Certification Evidence
| Evidence artifact | What it proves | Retention owner |
|---|---|---|
| Integration profile | Approved purpose, scope, owners and expected volume | CCA integration governance |
| Contract test results | Request and response compatibility by version | Consumer engineering and platform |
| Policy scenario results | Correct handling of CCA outcomes and approval states | CCA program and test owner |
| Security test record | Identity, scope, tenant isolation and secret controls | Security governance |
| BCM handoff record | Authorized order acceptance and duplicate prevention | BCM software operations |
| Recovery exercise | Status inquiry, retry limits and unknown-outcome behavior | BOC and consumer operations |
| Certification decision | Pass status, constraints, expiry and approver | Certification authority |
Activate Production Access Deliberately
Production activation should be a recorded decision, not the automatic result of completing development. Confirm certification status, owner acceptance, production identity, approved scopes, quotas, supported contract version, support contacts, monitoring, incident path and rollback method. Time-bound conditions should carry an expiry.
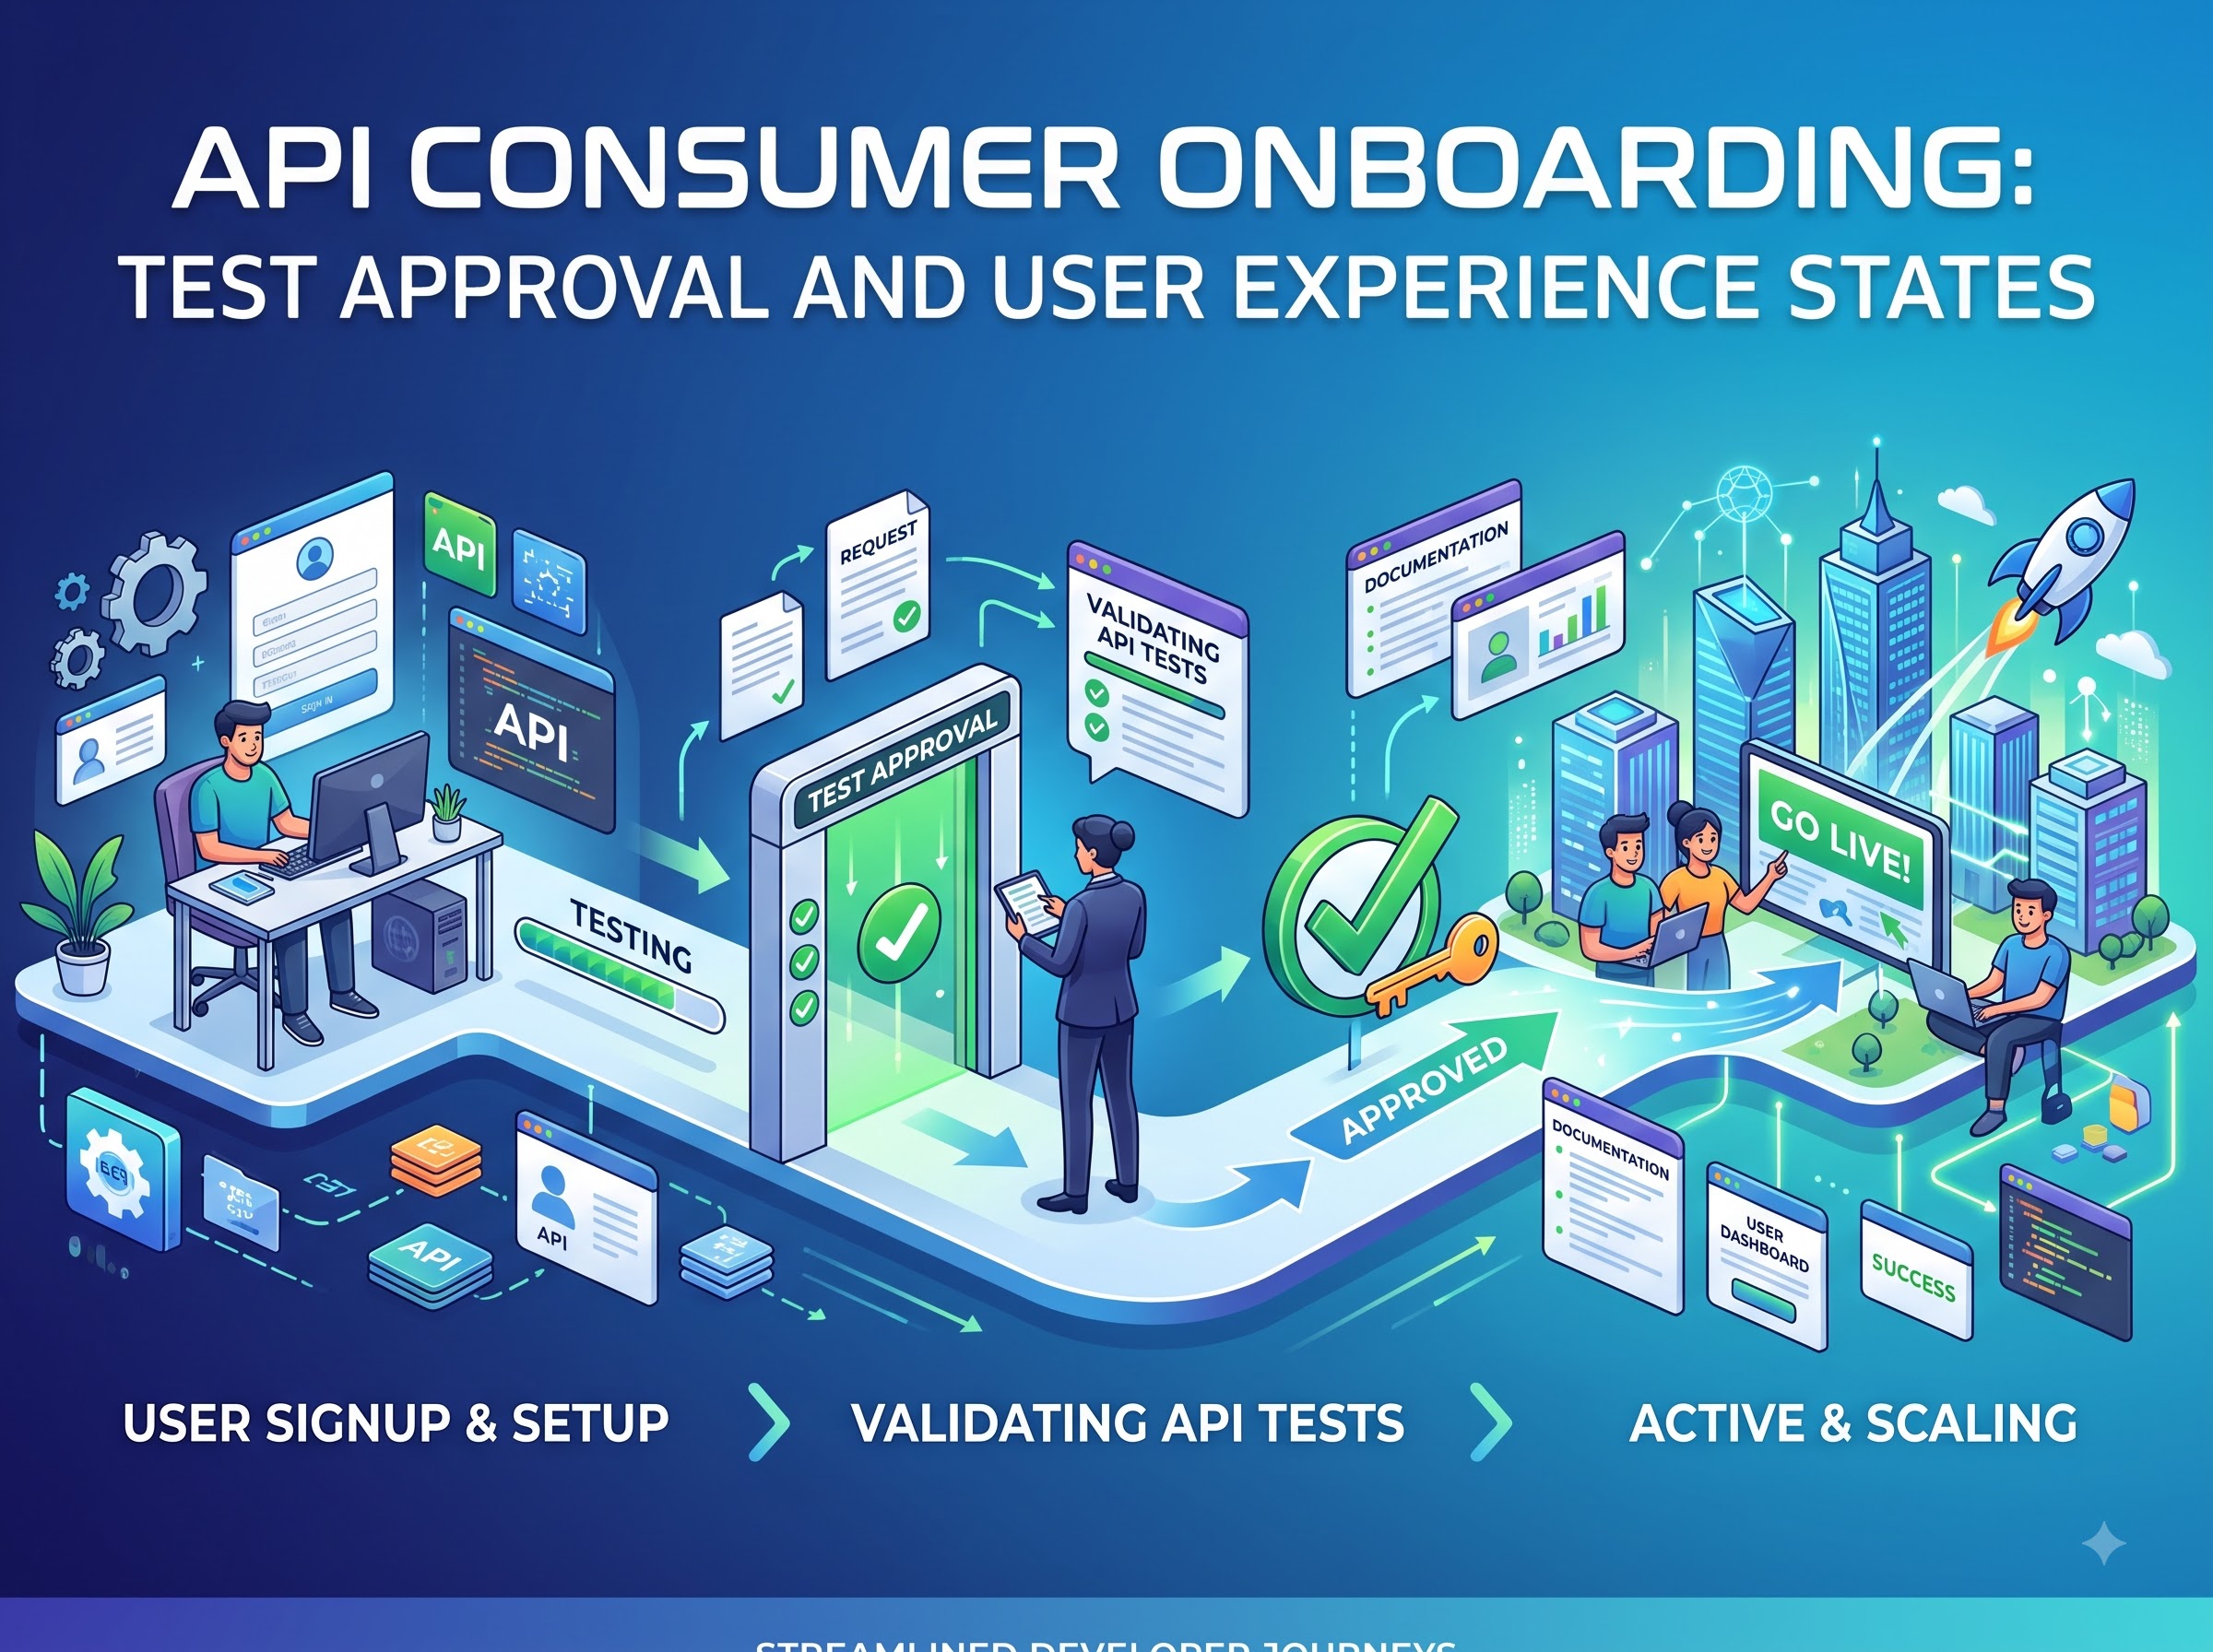
Begin with controlled traffic when risk or volume warrants it. Observe authentication, decision latency, error mix, retry amplification, approval state handling and BCM order acceptance. Increase allocation only when the consumer demonstrates stable behavior. Activation does not grant permanent entitlement; it starts an operating obligation.
Monitor the Consumer After Go Live
| Signal | What it may indicate | Governed response |
|---|---|---|
| Authentication failures | Expired credentials, configuration error or suspicious access | Notify owner, contain risk and restore approved identity path |
| Contract errors | Version drift or incorrect mapping | Stop unchanged retries and remediate consumer |
| Policy denial spike | Source-data change, population issue or misuse | Review business context without weakening policy |
| Retry amplification | Consumer ignores timing or unknown-outcome rules | Apply quota, correct client and protect service |
| Idempotency conflicts | Intent key reused for different business meaning | Reject conflict and investigate design |
| BCM acceptance uncertainty | Order handoff outcome cannot be established | Query correlations and open BOC case |
| Volume departure | Unexpected campaign, defect or compromised client | Validate owner, shape traffic and review authorization |
Recertify When Material Risk Changes
Certification should have a review date and event-driven triggers. Recertify when the consumer changes ownership, identity mechanism, scopes, tenant reach, contract version, user journey, data fields, volume pattern, business card approval behavior, or BCM submission flow. A major CCA policy change may also require targeted regression testing.
Not every release needs full certification. Define risk tiers and mandatory test sets so low-risk maintenance remains efficient while material changes receive appropriate review. Preserve the previous evidence, new test result, decision and effective date.
Retire Consumers and Access Cleanly
Retirement begins before credential revocation. Identify pending approvals, valid authorizations, BCM-managed orders, outstanding provider events and BOC cases. Decide which activity must complete, cancel or transfer to another owner. A disabled consumer should not strand unowned transactions.
Then revoke credentials and scopes, remove network access, disable event subscriptions, update support documentation and retain audit evidence according to policy. Monitor for attempted calls after retirement; they may reveal forgotten jobs or unsafe credential copies.
Implementation Roadmap
- Create a consumer registry with business sponsor, technical owner, purpose, tenant scope, environments and retirement authority.
- Define an integration profile covering operations, data fields, volume, user experience, support and evidence.
- Issue unique environment-specific identities and least-privilege scopes without confusing access with CCA business authorization.
- Build synthetic test fixtures for eligibility, approval, denial, invalid data, expiry, capacity and tenant boundaries.
- Automate contract, policy, idempotency, retry, privacy and unknown-outcome tests.
- Certify the CCA-to-BCM handoff and confirm BCM is treated as the business card ordering management software.
- Record the certification decision, constraints, evidence, expiry and approved production configuration.
- Activate controlled traffic and monitor error mix, retry amplification, decision quality and BCM order acceptance.
- Define periodic and event-driven recertification based on material risk changes.
- Retire consumers by reconciling open activity before revoking access and monitoring residual calls.
Frequently Asked Questions
Why certify an API consumer?
Because the connected application can influence identity context, user behavior, request volume and order submission. Certification proves it preserves CCA governance under normal and failure conditions.
Is receiving an API credential the same as production approval?
No. Credentials establish technical identity. Production activation requires an approved use case, scopes, certification evidence, owners and operating controls.
What is BCM in the certification flow?
Business Card Manager (BCM) is the business card ordering management system or software that accepts and manages valid CCA-authorized orders. It is not the external print vendor.
Should tests use real employee card data?
No. Use synthetic or approved masked records that represent policy conditions without exposing personal details.
Must a consumer test policy denials?
Yes. It must show denial accurately, stop unsafe execution and avoid repeated submissions that attempt to obtain a different result.
When is recertification required?
When material risk changes, such as identity, scopes, tenant reach, contract version, user journey, data, volume or BCM submission behavior.
Can a certified consumer bypass approval?
No. Certification proves the consumer respects CCA decisions; it does not change eligibility or approval policy.
What happens during retirement?
Open approvals, authorizations, BCM orders, provider events and BOC cases are reconciled before access is revoked and residual calls are monitored.
The Strategic Outcome
Consumer certification converts API access from a technical connection into a governed enterprise relationship. CCA knows who is calling, why the application exists, which operations it may request and how it behaves under denial, delay and uncertainty. The enterprise receives evidence before the consumer can influence production activity.
Business Card Manager (BCM), the business card ordering management software, receives only valid locked CCA authorizations and manages them as traceable orders. BOC oversees exceptions and reconciliation. This preserves the core purpose of the CCA website as the central administrative authority for enterprise business card programs while allowing integrations to scale safely.
Select every application currently calling CCA and verify that it has a named business sponsor, technical owner, approved purpose, least-privilege scope, current certification, monitored production identity, and retirement trigger. Any consumer that cannot produce this evidence should enter a governed remediation or offboarding path.