Enterprise Business Card Integration Discovery
Building a qualified CCA solution blueprint before implementation begins
Discovery Turns Interest into an Implementable Decision
An enterprise may know that it wants to connect an HCM, identity platform, CRM, ERP, procurement system or service portal to business card ordering. However, that intention is not yet an integration scope. First, the organization must identify the business trigger, authoritative data, permitted action, security boundary, approval path, ordering workflow, fulfillment route and evidence required to prove the outcome.
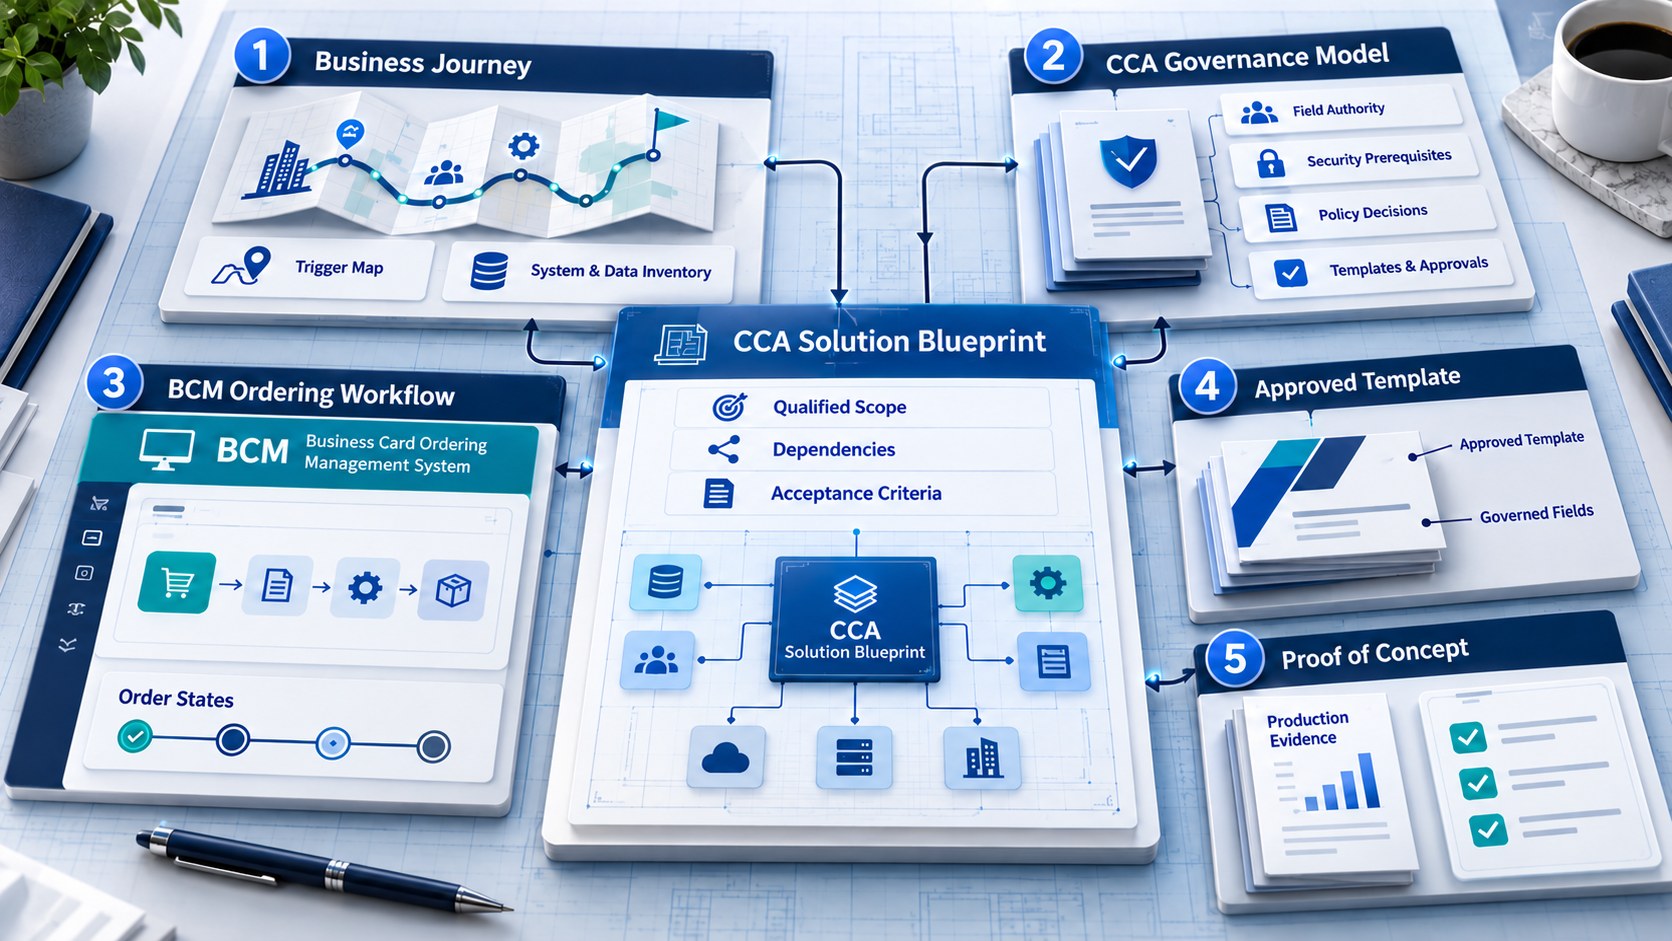
An integration discovery therefore creates this shared understanding before design and build begin. As a result, it replaces platform-level assumptions with a qualified CCA solution blueprint. The blueprint then explains what will connect, why the business needs the connection, what Color Card Administrator will govern, how Business Card Manager will execute the order and which prerequisites the team must resolve before anyone commits to delivery.
Keep the Purpose of CCA at the Center
CCA is the enterprise orchestration and control layer for API-integrated business card printing and management. In practice, it connects approved information from enterprise systems to centralized permissions, identity rules, templates, approvals, ordering, reporting, production and fulfillment. Discovery should therefore begin with the control outcome, not with a catalog of endpoints.
First, the source system remains authoritative for its domain. Meanwhile, CCA determines how approved facts may influence business card identity and ordering. BCM is the business card ordering management system or software that manages permissions, approvals, templates, quantities, orders and reporting. Finally, production and fulfillment execute the physical result. Therefore, a strong discovery protects these boundaries from the beginning.
Start with One Complete Business Journey
The most productive starting point is therefore a real journey rather than a generic request to connect two systems. For example, the journey may involve preparing a card for a new hire, updating a card after a promotion, initiating an approved request from ServiceNow, applying a cost center from ERP or routing a sales-role change from CRM. As a result, every stakeholder examines the same transaction.
| Journey question | Decision required | Blueprint output |
|---|---|---|
| What starts the process? | An event, request or schedule, as well as an administrator action | Named trigger and initiating system |
| Who or what is affected? | A person, such as an employee or contractor, or a team, entity or program | Stable subject and organizational scope |
| What may change? | Eligibility, fields, template, quantity or fulfillment | An explicit governed action rather than an assumption |
| Who must approve? | Owners such as manager, brand, procurement or exception owner | Approval route as well as accountability |
| What completes the journey? | Order, production, shipment, delivery or cancellation | Authoritative final state as well as evidence |
Bring the Right Stakeholders into Discovery
| Stakeholder | Knowledge contributed | Decision responsibility |
|---|---|---|
| Business program owner | Purpose and populations, as well as service levels and outcomes | Priorities as well as the acceptable operating model |
| HR or source owner | Worker data and lifecycle events, as well as field meaning | Approved workforce use and authority |
| Identity and security | Authentication and authorization, as well as credential policy | Access model and security acceptance |
| Brand and communications | Identity presentation, templates and exceptions | Approved content as well as design controls |
| Procurement and finance | Cost objects and budgets, as well as purchasing and reconciliation | Financial governance and reporting |
| CCA and BCM administrators | Programs and permissions, as well as approvals and order states | Governance configuration and operations |
| Integration and architecture | Interfaces and middleware, as well as monitoring and support | Technical pattern and ownership |
| Production and fulfillment | Proof and manufacturing, as well as shipping and delivery | Provider route and returned status |
Map the Current State Without Preserving Its Weaknesses
First, discovery should document how teams handle requests today: where people copy information, who checks it, which templates they use, how approval occurs, how orders reach production and how status returns. This review then reveals manual handoffs, duplicate entry, inconsistent rules, invisible exceptions and unsupported local workarounds.
However, the goal is not to automate every existing step. Some steps exist only because the systems do not connect. Others, in contrast, hide an important control that must remain. Therefore, classify each activity as an authoritative fact, governance decision, operational execution, evidence requirement or avoidable workaround. The future design can then simplify the process without discarding accountability.
Confirm Integration Status and Customer Prerequisites
CCA distinguishes an existing integration from a platform that is available for configured integration. For an available integration, the organization and CCA must therefore confirm whether the customer environment supports the required method. In addition, final scope can depend on subscription, tenant configuration, API entitlement, permissions, security requirements, middleware, data access and the desired workflow.
Consequently, discovery should record evidence rather than assumptions: the relevant product edition, enabled service, authentication option, API or export documentation, sandbox availability, administrative owner, approval process and known limits. After all, a public API does not prove that a particular customer account has the necessary access.
Assess Technical Feasibility
| Assessment area | Questions to answer | Qualified result |
|---|---|---|
| Interface | Is a supported API, event, report, file or middleware route available? | The selected connection pattern as well as its constraints |
| Authentication | How will the workload prove its identity? | An approved credential or, alternatively, a managed identity model |
| Authorization | Which records, fields and actions does the policy permit? | Least-privilege scopes as well as tenant boundaries |
| Volume and timing | How many records, how often and with what latency? | Rate and batch assumptions, as well as event and capacity limits |
| Environment | Are sandbox and nonproduction data paths available? | Test strategy as well as environment dependencies |
| Reliability | How does the integration handle timeouts, retries, duplicates and late events? | Idempotency as well as recovery behavior |
| Change | Who communicates schema, API and configuration changes? | Version ownership as well as a compatibility plan |
Assign Authority for Every Business Card Field
Discovery must identify which system owns each field used on a card or in an ordering decision. For example, HCM may own employment status, legal entity and job information. Similarly, a directory may supply approved contact information. CRM may also contribute a governed customer-facing role. Likewise, ERP may own cost center. Meanwhile, CCA owns the rules that determine whether and how those values may appear.
Next, for each field, document source, meaning, format, effective date, allowed transformation, fallback and exception owner. Also, if two systems disagree, the blueprint must state which source prevails and whether automation may continue. As a result, the integration cannot quietly turn the most recent or easiest value into the public business identity.
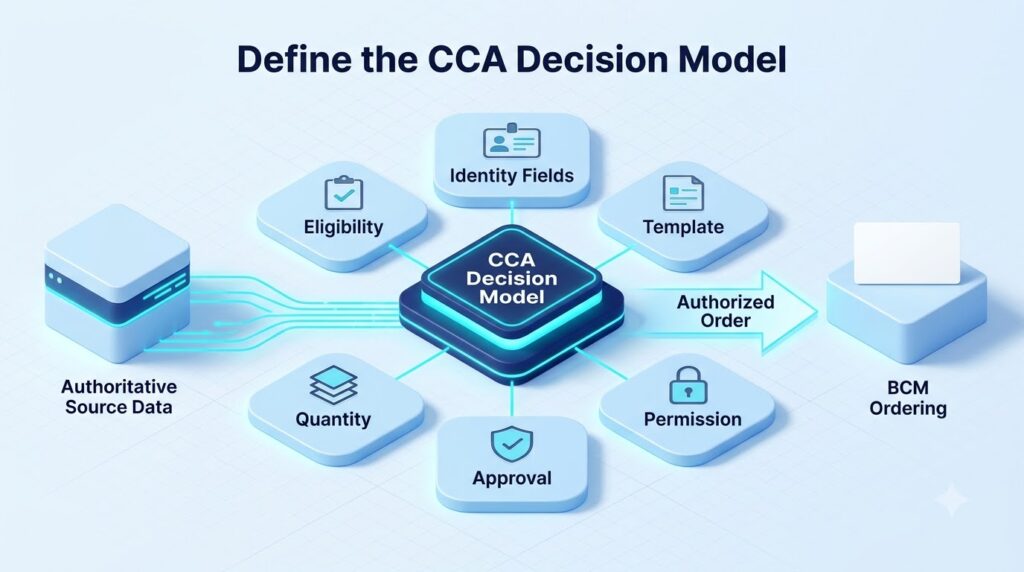
Define the CCA Decision Model
| CCA decision | Discovery inputs | Blueprint definition |
|---|---|---|
| Eligibility | Population, role, employment type, entity and lifecycle state | Allowed and denied conditions, as well as review-required cases |
| Identity fields | Authoritative values, presentation rules and overrides | Locked and selectable fields, as well as exception-controlled fields |
| Template | Brand, entity, region, language and card type | Permitted template family as well as version behavior |
| Permission | Requester, delegate, approver and administrator roles | Action and scope matrix |
| Approval | Risk, quantity, change type and organizational hierarchy | Required route, as well as escalation and expiry |
| Quantity | Role, event, inventory and policy limits | Default and maximum limits, as well as exception rules |
| Provider route | Location, product, service level and capacity | Authorized production and fulfillment path |
Design the Handoff to BCM
Therefore, CCA should send BCM a complete, authorized ordering specification rather than an unresolved set of source attributes. In particular, the handoff includes the business key, subject, program, approved fields, template, quantity, approval state, provider route and decision evidence. BCM then preserves the managed transaction and stops downstream execution from reinterpreting policy.
Discovery should also define BCM states and actions: draft, pending approval, approved, submitted, held, in production, shipped, delivered, cancelled or failed. In addition, it should identify which system may advance each state and how teams reconcile the order when a response arrives late or remains uncertain.
Map Production Fulfillment and Return Evidence
However, a business card integration is incomplete if discovery stops at order submission. After all, physical execution introduces proof, manufacturing, shipment, delivery, cancellation and reprint states. The blueprint therefore identifies the production interface, provider identifiers, status vocabulary, delivery data, retry boundaries and exception ownership.
Next, the integration should normalize returned events and correlate them to the source event, CCA decision and BCM order. Business Ops Center can then make status, exceptions and reconciliation visible across the workflow. Finally, the evidence chain should prove that the delivered outcome matched the approved identity and order.
Protect Security and Privacy by Design
| Control area | Discovery requirement | Blueprint outcome |
|---|---|---|
| Data minimization | Identify the minimum attributes required for each decision | A field allowlist as well as prohibited data |
| Access control | Separate request, approve, administer and report privileges | Role and scope model |
| Credential handling | Define issuance, storage, rotation and revocation | Accountable secret or identity lifecycle |
| Transport and events | Confirm encryption, signing and replay protection | A protected API as well as a webhook pattern |
| Logging | Capture useful evidence rather than unnecessary personal data | Redacted operational records as well as audit records |
| Retention | Align records with business, privacy and legal requirements | State-specific retention as well as disposal rules |
| Incident response | Name owners for access, data and ordering failures | Escalation and containment, as well as a recovery path |
Prioritize Use Cases with a Qualification Score
However, the team should not implement every potential connection at once. Instead, score each journey against business value, transaction volume, data quality, control improvement, technical feasibility, security readiness, exception complexity and operational ownership. For example, a high-volume process is not a good first pilot if authoritative fields remain unresolved or teams cannot reconcile production outcomes.
| Qualification factor | Strong candidate | Warning sign |
|---|---|---|
| Business outcome | A specific measurable problem as well as an accountable sponsor | A generic desire to automate rather than a defined problem |
| Data authority | Owners and meanings have documentation | Conflicting or unowned fields |
| Access feasibility | Approved interface and permissions are available | Unknown subscription or access restrictions |
| Governance fit | The team can define CCA rules and exceptions | A source system that bypasses CCA policy instead of following it |
| Execution fit | Teams understand BCM and provider states | Order or production state remains ambiguous |
| Operational ownership | Named support owners as well as exception owners exist | No team owns failures or changes |
| Evidence | Teams can correlate and reconcile the outcome | Success measured by API response rather than business outcome |
Build a Proof of Concept that Tests Governance
Therefore, a proof of concept should test the riskiest assumptions, not merely show that two endpoints can exchange JSON. To do this, use a bounded population, controlled templates and nonproduction fulfillment where possible. Also include a normal request, an ineligible subject, a field conflict, an approval requirement, a duplicate event, a delayed response and a returned status.
Ultimately, the proof succeeds when CCA makes the expected decision, BCM creates no more than one managed order, unauthorized paths remain blocked and the team can explain every outcome. In addition, the team should record any manual intervention so the final scope reflects real operating effort.
Create the Integration Discovery Deliverables
| Deliverable | Contents | Decision supported |
|---|---|---|
| Journey map | Trigger, actors, decisions, execution and final evidence | Shared current-state as well as target-state understanding |
| System context | Applications, tenants, interfaces and owners | Architecture boundary as well as dependencies |
| Authority matrix | Fields, sources, transformations and conflicts | Identity integrity as well as data governance |
| CCA policy model | Eligibility, templates, permissions, approvals and routing | Governed automation scope |
| BCM state model | Order actions, states, holds and reporting | Managed transaction behavior |
| Security profile | Credentials, scopes, data, logs and retention | Security review as well as controls |
| Qualification record | Assumptions, risks, dependencies and score | Go, revise, defer or stop decision |
| Implementation outline | Phases, owners, tests, acceptance and support | Scope and sequencing, as well as delivery planning |
Run the Discovery in Structured Stages
- First, select one high-value business journey and name its accountable sponsor.
- Next, map the current process from source fact through delivered business card.
- Then identify every system, tenant, interface, owner and operational dependency.
- After that, confirm integration status, customer entitlement, permissions and security prerequisites.
- Next, assign authoritative ownership and transformation rules for every required field.
- Then define CCA eligibility, identity, template, permission, approval, quantity and routing decisions.
- Similarly, define the authorized handoff and lifecycle states managed by BCM.
- After that, map production, fulfillment, returned events, exceptions and reconciliation.
- Next, choose the technical pattern and document volume, timing, reliability and change assumptions.
- Then score the use case and design a bounded proof of concept for the highest-risk assumptions.
- Finally, publish the solution blueprint with scope, dependencies, acceptance criteria and owners.
Measure Discovery Quality
| Measure | What it proves | Target |
|---|---|---|
| Decision completeness | Every material rule has an owner as well as defined behavior | Complete before design approval |
| Assumption closure | Critical unknowns have evidence or an action owner | No unowned critical assumptions |
| Field authority coverage | Required data has documented provenance as well as conflict rules | Complete for pilot scope |
| Access readiness | Owners have approved or scheduled interfaces and permissions | No hidden entitlement dependency |
| Exception coverage | Failure and review paths have owners as well as safe actions | All high-consequence cases |
| Evidence coverage | Teams can correlate source, decision, order and outcome | End-to-end traceability |
| Scope confidence | Cost and timing rely on verified constraints rather than guesses | Qualified estimate range |
Frequently Asked Questions
What is business card integration discovery?
In short, it is a structured process that converts a desired enterprise connection into a qualified CCA governance, API, BCM ordering and fulfillment blueprint.
Why is discovery needed when a platform has an API?
Because an API alone does not confirm customer entitlement, data authority, security acceptance, workflow fit or downstream ordering behavior, discovery still matters.
What is the purpose of CCA?
In short, CCA centralizes orchestration, identity governance, templates, permissions, approvals, routing and evidence for enterprise business card execution.
What is BCM?
Simply put, BCM is the business card ordering management system or software that manages permissions, approvals, templates, quantities, orders and reporting.
Who should participate?
Ideally, the business owner, source owner, identity and security, brand, procurement, CCA and BCM administrators, integration architecture and fulfillment operations all take part.
What should the first discovery journey be?
First, choose a valuable, representative and bounded transaction with an accountable owner and measurable outcome.
Does discovery guarantee that a team can build the integration?
No. Instead, it identifies evidence, constraints, dependencies and risks so leaders can decide feasibility, scope, cost and timing responsibly.
What should a proof of concept test?
Above all, it should test governance, security, exceptions, idempotency, BCM order integrity and returned evidence, not only connectivity.
How can teams reduce personal data risks?
To reduce them, use field allowlists, least privilege, data minimization, protected credentials, redacted logs and explicit retention rules.
When is discovery complete?
When decision owners can approve a blueprint with verified prerequisites, clear responsibilities, acceptance criteria and managed risks.
The Strategic Outcome
In short, integration discovery gives the enterprise a defensible path from opportunity to implementation. It protects the purpose of CCA by keeping governance centralized, preserves the authority of source systems and ensures that BCM receives a complete, controlled order specification. Moreover, production, fulfillment and BOC evidence remain part of the design rather than afterthoughts.
As a result, the organization gets a scope that business, security, architecture and operations can evaluate together. The organization can then invest with clearer assumptions, select the right pilot, reduce rework and expand integrations through a repeatable discovery standard.
To begin, choose one platform and one business card journey for a focused discovery workshop. Then bring the system owner, security, brand, procurement, CCA and BCM administrators, and fulfillment operations. Finally, leave with a journey map, authority matrix, CCA policy model, BCM state model, feasibility record, proof-of-concept plan and named owners for every open dependency.