

Business Card API Access Certification and Periodic Review
Business Card API Access Certification Explained: Regular Reviews to Retain, Revise or Revoke Access
API access that made sense at launch can outlive its purpose. This video explains business card API access certification, a structured review that checks each connected system for registration, workload identity, data fields and permissions, then retains, revises or revokes its access, turning access from a permanent grant into a managed lifecycle.
Verifying connected systems, scopes, CCA permissions and BCM ordering authority over time.
Onboarding Is Not the End of Authorization
Teams may correctly register, scope and test a connected enterprise system when it first enters production. Over time, its business owner can change, a region can leave the program, a newer workflow can replace an old one, fields can become unnecessary or credentials can remain active after traffic stops. Without periodic certification, approved access gradually becomes inherited access that nobody can explain.
Business card API access certification is the structured review of each consumer, workload identity, permission, population, data field and action. It confirms that the connection still serves a valid business journey, CCA policies remain appropriate, BCM ordering authority has not expanded beyond need and operational teams can identify and support the integration. Finally, the review ends with an accountable decision to retain, reduce, suspend or remove access.
Keep CCA at the Center of the Review
Color Card Administrator is the enterprise orchestration and governance layer for API-integrated business card programs. Specifically, CCA determines how approved enterprise facts may influence eligibility, identity, templates, permissions, approvals, quantities and provider routing. An access review must therefore examine both technical scopes and the business decisions those scopes can trigger.
BCM is the business card ordering management system or software. It also manages permissions, approvals, templates, quantities, orders and reporting for authorized transactions. Business Ops Center, or BOC, provides operational visibility, exceptions and reconciliation. Ultimately, certification protects the separation between source-system facts, CCA authority, BCM execution and BOC oversight.
What Must Be Certified
| Certification object | Review question | Possible decision |
|---|---|---|
| Consumer registration | Does the business journey still exist? | Retain, revise or retire the consumer |
| Business owner | Is an accountable sponsor still assigned? | Confirm or transfer ownership |
| Workload identity | Is the identity unique, active and monitored? | Retain, rotate, suspend or revoke |
| Population scope | Are entities, regions and programs still required? | Keep or narrow the population |
| Data scope | Are all fields still necessary and authoritative? | Keep, minimize or correct authority |
| Action scope | Are requested operations still justified? | Keep, reduce or remove actions |
| CCA policy rights | Do decisions remain aligned with approved policy? | Recertify or remediate configuration |
| BCM ordering rights | Can only approved transactions reach execution? | Retain, restrict or hold activation |
Build an Authoritative Access Inventory
First, certification depends on a complete inventory. Next, combine consumer registrations, workload identities, credentials, API scopes, CCA configuration, BCM permissions, network routes, middleware jobs and observed traffic. In addition, the record should show the consumer, owner, environment, tenant, population, data, actions, policy version, credential lifecycle, last use and operational contact.
However, do not treat configuration alone as proof of use. Then compare granted rights with actual activity and approved business journeys. A rarely used seasonal integration may remain valid, while a high-traffic connection may be operating outside its approved purpose. Teams should investigate unknown credentials or traffic before certification closes.
Assign Accountable Reviewers
| Reviewer | What they certify | Evidence expected |
|---|---|---|
| Business owner | Purpose, population and required outcomes | Current journey, sponsorship and service need |
| Source owner | Field authority and permitted data use | Data definition, provenance and quality |
| CCA owner | Eligibility, identity, template and approval policy | Policy mapping and decision evidence |
| BCM owner | Ordering permissions, states and reporting access | Managed transaction and role records |
| Security owner | Identity, credential, scope and tenant controls | Access tests, rotation and monitoring |
| Operations owner | Alerts, exceptions, reconciliation and support | BOC dashboards, runbooks and ownership |
| Provider owner | Production and fulfillment routing | Authorized provider and returned-status evidence |
Certify Business Need Before Technical Access
Above all, begin with the journey, not the token. In other words, the reviewer should understand which event or request starts the process, who or what is affected, which CCA decision is needed, what BCM transaction follows and which outcome proves completion. If the journey has ended, the access should not survive simply because it causes no visible incident.
Next, confirm that the current owner accepts responsibility for change, incident response and offboarding. Governance teams should suspend a consumer without an accountable owner or place it under a time-bound remediation plan. Reviewers cannot infer ownership from the last developer who changed the integration.
Review Population and Tenant Boundaries
For example, an integration may have started with one entity or region and later gained a broader scope for convenience. Therefore, certification should compare the approved population with both configured access and observed records. Then test that the workload cannot reach another tenant, entity, program or employee population outside its purpose.
Where populations change frequently, derive boundaries from governed attributes rather than static lists. CCA should still apply the authoritative policy at decision time. A consumer may provide the context, but it should not decide that a new population is eligible merely because the source can return it.
Minimize Data and Reconfirm Authority
| Data review | Certification test | Control outcome |
|---|---|---|
| Required fields | Is each field necessary for an approved decision or order? | Remove unused attributes |
| Authoritative source | Does the supplying system still own the meaning? | Confirm or remap provenance |
| Transformation | Are formatting and fallback rules still approved? | Retain, update or remove transformation |
| Conflicts | What happens when two sources disagree? | Apply documented priority or review |
| Sensitive values | Are logs and payloads exposing unnecessary data? | Redact and minimize evidence |
| Retention | Are records kept only for approved periods? | Align storage and disposal |
| Outbound status | Does the consumer receive only required outcomes? | Restrict response and event fields |
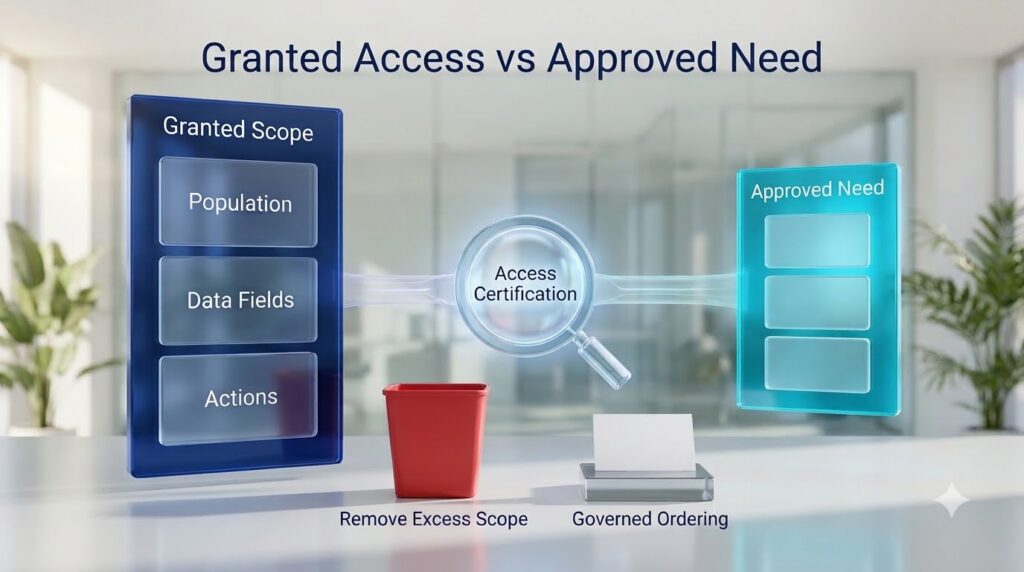
Certify Actions, Not Just Read Access
In particular, the highest-risk permissions are actions that can change public identity, approve a request, alter quantity, select a provider, cancel an order or initiate a reprint. Therefore, review each operation against the consumer journey and the separation of duties expected by the enterprise. A system that only supplies employee facts should not hold execution rights.
Equally important, negative tests are essential. For instance, attempt an out-of-scope record, unauthorized template, excessive quantity, unapproved field override and prohibited provider route. In turn, CCA should deny or route the action for review, and BCM should create no executable order from an unauthorized decision.
Verify Workload Identity Health
| Identity control | Review evidence | Remediation trigger |
|---|---|---|
| Uniqueness | One identity maps to one consumer and environment | Shared or unidentified use |
| Least privilege | Granted scopes match approved data and actions | Unused or excessive scope |
| Credential storage | Secrets or keys use approved protection | Code, ticket or unmanaged storage |
| Rotation | Credential changes have succeeded on schedule | Overdue or untested rotation |
| Monitoring | Use can be attributed and anomalous access detected | Missing logs or unexplained activity |
| Revocation | Access can be disabled promptly and safely | No tested removal path |
| Recovery | Replacement identity and incident steps are owned | Unclear emergency procedure |
Review CCA Policy Permissions
A technical scope may appear unchanged while CCA policy has expanded. Next, review which programs, templates, fields, approval paths, quantity limits and provider routes the consumer can influence. Next, compare current configuration with the last approved certification and explain every difference. Notably, effective-dated policy versions make this review more defensible.
Then test representative allowed, denied and review-required scenarios. Certification should confirm that missing, stale or conflicting data still produces the approved safe behavior. If a consumer can now supply a new field or value, the review must determine whether CCA has an explicit policy for it rather than allowing a default path.
Review BCM Ordering Authority
BCM should continue to receive a complete, authorized order specification from CCA. Review whether the consumer can create, update, approve, cancel or reprint orders and whether the business journey still requires those actions. Also confirm that template, quantity, approval state, provider route, correlation identifier and policy version remain protected through the transaction.
Additionally, use order and reporting evidence to identify dormant permissions and unexpected behavior. Likewise, replayed events should not create duplicates. Similarly, denied decisions should not produce executable transactions. Reporting access should follow the same population and data boundaries as ordering access unless a separately approved need exists.
Use Operational Evidence to Challenge Assumptions
| Operational signal | What it may reveal | Review response |
|---|---|---|
| No traffic | Dormant integration or seasonal journey | Confirm need or suspend access |
| Unexpected population | Scope drift or source change | Investigate and narrow boundary |
| High denial rate | Poor data quality or incorrect consumer behavior | Remediate mapping or policy |
| Duplicate attempts | Retry or correlation weakness | Fix idempotency before recertification |
| Manual overrides | Policy gap or operational workaround | Define governed exception path |
| Unresolved states | Provider or BCM lifecycle mismatch | Reconcile and assign ownership |
| Unowned alerts | Support transfer or incomplete handoff | Restore accountable response |
Set a Risk-Based Review Frequency
Not every consumer needs the same schedule. Instead, review frequency should reflect action risk, data sensitivity, population size, transaction volume, provider impact, exception history, credential model and rate of change. A consumer that can initiate production or update identity fields requires more attention than a read-only reporting integration with limited data.
Moreover, material changes should trigger an out-of-cycle review. Examples include a new source, tenant, entity, action, template family, approval model, provider, credential method or business owner. Of course, certification is not a substitute for change approval; it is the recurring proof that the approved design remains true.
Record a Clear Certification Decision
| Decision | Meaning | Required follow-through |
|---|---|---|
| Certify | Purpose, owner and access remain appropriate | Record evidence and next review date |
| Certify with action | Access may continue while a bounded gap is corrected | Owner, due date and compensating control |
| Reduce | Some populations, data or actions are unnecessary | Remove scope and verify behavior |
| Suspend | Access should stop until a risk or ownership gap is resolved | Block new use and protect in-flight orders |
| Revoke | Business need ended or access is unacceptable | Remove credentials, routes and permissions |
| Investigate | Evidence is insufficient or activity is unexplained | Time-bound review with restricted access |
Remediate Without Breaking In-Flight Orders
Removing access can affect requests awaiting approval, orders in production and provider statuses returning after an administrator disables the consumer. Accordingly, the remediation plan should distinguish new requests from existing transactions. CCA can stop new authorization while BCM preserves managed order history and controlled completion, cancellation or hold behavior.
Revoke credentials and routes only after identifying legitimate late events or alternative status paths. Afterward, BOC can help reconcile affected orders and exceptions. The goal is to reduce unnecessary access without losing accountability for physical work already authorized.
Make BOC Part of Continuous Certification
In addition, BOC can provide the operational evidence used between formal reviews: consumer activity, authentication failures, CCA decisions, BCM order states, provider responses, exceptions and reconciliation. Dashboards should segment results by consumer, credential, policy version, program and population so teams can detect drift early.
Automated signals can trigger review, but they should not certify access by themselves. A dashboard can show use; it cannot decide that the use remains necessary or properly owned. However, the final decision belongs to accountable business, governance, security and operational reviewers.
Implement Access Certification in Practical Stages
- First, build the inventory of consumers, owners, identities, credentials, scopes, policies and observed use.
- Next, assign business, source, CCA, BCM, security, operations and provider reviewers.
- Then confirm the business journey, population, service need and accountable ownership.
- After that, compare granted tenant, data and action scopes with approved requirements and actual activity.
- Reconfirm authoritative sources, transformations, conflicts, minimization and retention.
- Test workload identity, least privilege, revocation and negative authorization paths.
- Review CCA policy permissions and BCM ordering authority using decision and transaction evidence.
- Finally, record certify, reduce, suspend, revoke or investigate decisions with owners and dates.
- Remediate access while protecting in-flight orders and preserving audit evidence.
- Use BOC signals to monitor drift and schedule the next risk-based certification.
Measure Certification Quality
| Measure | What it proves | Target direction |
|---|---|---|
| Inventory coverage | All active identities and consumers are known | Complete before review launch |
| Owner coverage | Every consumer has accountable business and technical owners | Complete |
| Excess scope | Granted populations, data or actions lack current need | Decrease to zero |
| Dormant access | Unused credentials or consumers remain active | Decrease to zero |
| Decision completion | Review objects receive a documented outcome | Complete by deadline |
| Remediation age | Certified gaps remain unresolved | Decrease |
| Recurrence | Previously removed access returns without approval | Approach zero |
Frequently Asked Questions
What is business card API access certification?
It is the periodic confirmation that a connected system, identity, scope and action remain necessary, owned and properly governed through CCA.
Why is CCA central to certification?
CCA determines how approved enterprise facts may influence business card identity, eligibility, templates, approvals, quantities and routing.
What is BCM?
BCM is the business card ordering management system or software that manages permissions, approvals, templates, quantities, orders and reporting.
Who should certify access?
Business, source-data, CCA, BCM, security, operations and provider owners certify the areas they control.
How often should teams review access?
Use a risk-based schedule and trigger an additional review after material changes to purpose, owner, scope, policy or provider.
Does observed traffic prove the consumer needs access?
No. Activity proves use, but the owner must still confirm that the use is approved and necessary.
What happens when no one owns the consumer?
Suspend or restrict access under a time-bound investigation rather than silently accepting orphaned authorization.
Can teams reduce access without stopping current orders?
Yes. Stop new authorization while BCM preserves controlled handling and BOC reconciles in-flight transactions.
What evidence should teams retain?
Keep the inventory, reviewer decisions, tests, policy versions, BCM records, remediation and next review date.
When should teams revoke access?
Revoke it when the journey ends, ownership disappears, risk is unacceptable or required remediation is not completed.
The Strategic Outcome
In short, access certification prevents yesterday’s valid integration from becoming today’s unexplained authority. It also keeps source systems accountable for their data, CCA accountable for governance decisions and BCM limited to complete, authorized orders. BOC supplies operational evidence without replacing accountable review.
The enterprise reduces dormant credentials, excessive scopes and policy drift while preserving continuity for legitimate business journeys. As a result, periodic review turns integration access into a managed lifecycle rather than a permanent technical entitlement.
First, select the highest-risk business card API consumer and run a complete certification. Verify its purpose, owner, workload identity, population, data, actions, CCA policy permissions, BCM ordering rights and BOC operational evidence. Record a clear decision and remediate every unnecessary entitlement with an accountable deadline.