

API Observability For Enterprise Business Card Ordering
Observability Must Protect the Purpose of CCA
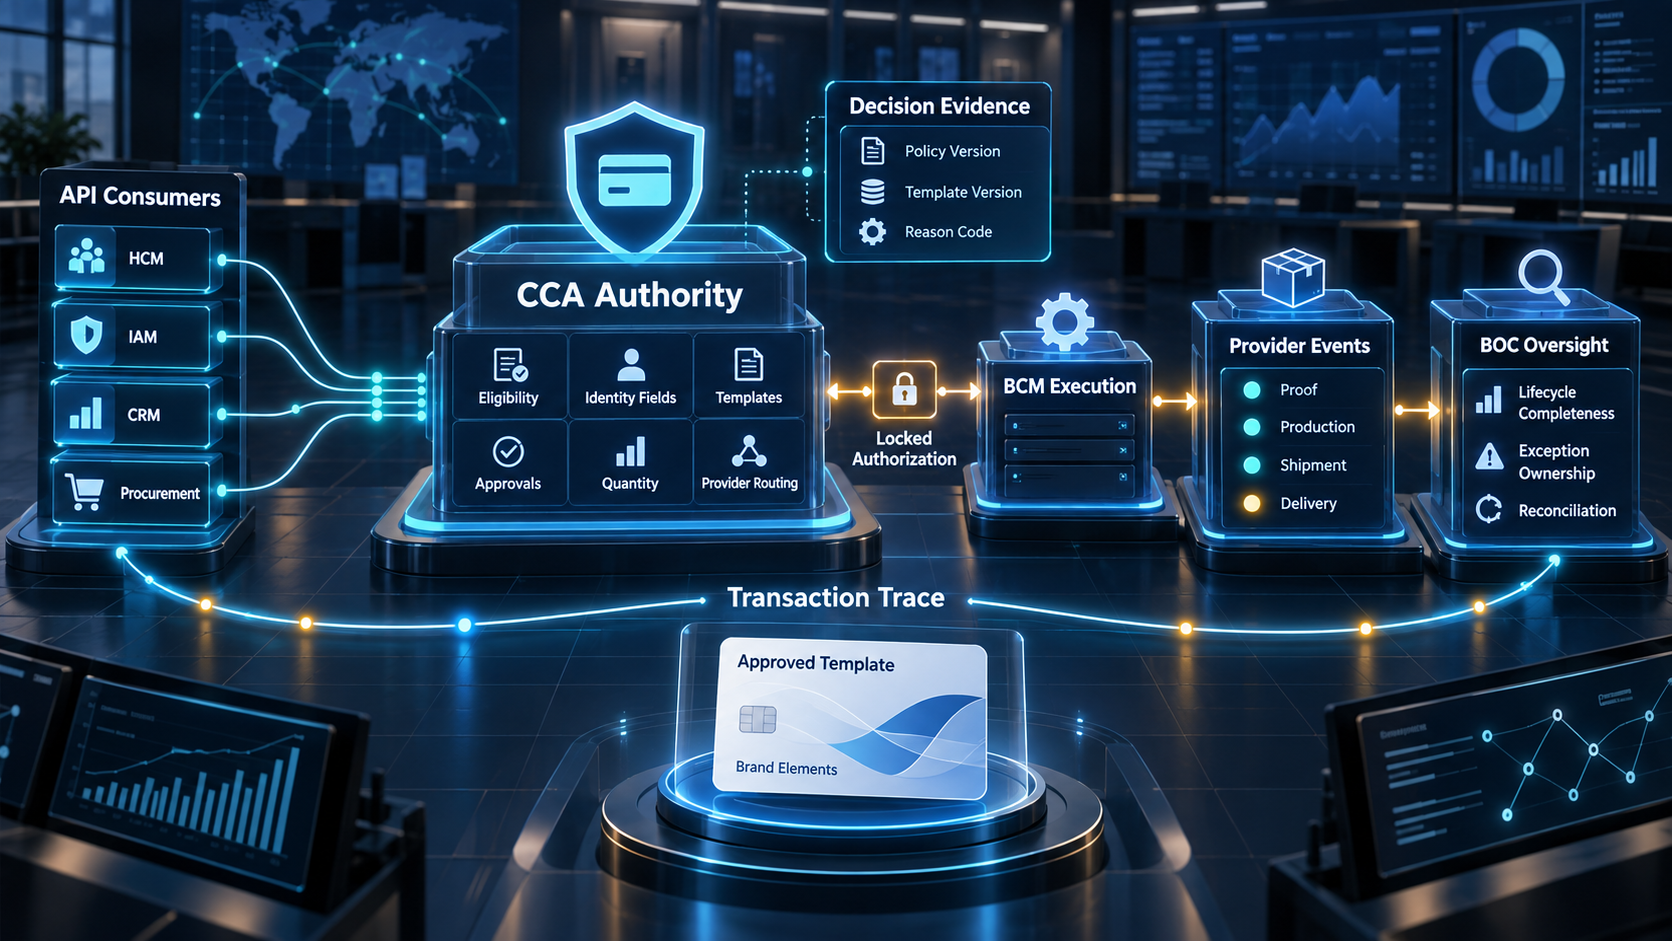
Enterprise business card ordering can involve an employee portal, HCM platform, identity provider, CRM, procurement system, API gateway, integration platform, Color Card Administrator (CCA), Business Card Manager (BCM), print suppliers, and Business Ops Center (BOC). Traditional monitoring may show whether each service is available, but it may not show whether the correct employee was eligible, the approved identity fields were used, the current template was selected, the right approval was applied, or the authorized order reached the intended provider.
CCA exists to centralize those business decisions. It is the authority for eligibility, identity fields, templates, quantities, approvals, destinations, provider routing, and exceptions. Observability should make that authority visible and explainable across connected channels. BCM executes the locked authorization, while BOC monitors lifecycle completeness, owns operational exceptions, and reconciles the outcome. The goal is not more dashboards. It is evidence that every business card governance transaction remained governed from request to delivery.
Technical Health and Governance Health Are Different
An API can return a successful status while producing the wrong business outcome. A connector may submit an outdated location. A mapping may replace an authoritative title with a user-entered value. An approval service may acknowledge a request after the underlying decision has expired. A supplier may accept an order created from an obsolete template. None of these failures is adequately described by uptime, latency, or error rate alone.
Technical health asks whether components responded within their expected service levels. Governance health asks whether the request was permitted, which policy and data sources shaped the decision, whether execution matched the authorization, and whether the final outcome reconciled. Enterprise observability needs both views, joined by durable identifiers rather than interpreted through disconnected logs.
The Observability Responsibility Model
| Layer | What it observes | What it must prove | Primary evidence |
|---|---|---|---|
| API gateway | Caller admission route quotas latency and response codes | Only registered identities and permitted scopes reached the capability | Client identity route scope result and trace ID |
| Integration layer | Message movement transformations, retries, and queues | Approved mappings preserved provenance and did not create policy | Flow version source reference and execution result |
| CCA authority | Eligibility fields, template approvals, quantity routing, and exceptions | The business action was authorized for the current identity and context | Decision ID reason policy and template versions |
| BCM execution | Proof order submission, production shipment and delivery | The locked authorization was executed without reinterpretation or duplication | Authorization hash order ID and lifecycle states |
| Provider adapter | Supplier acknowledgments status translation and errors | Provider events remained correlated and semantically normalized | Adapter version raw event reference and normalized state |
| BOC oversight | Exceptions service levels ownership and reconciliation | Every material failure was owned and every outcome matched to authority | Exception owner closure evidence and reconciliation result |
Start with a Canonical Transaction Identity
Observability breaks down when each platform invents a separate identifier. The portal may know a request number, the gateway a trace, CCA a decision, BCM an order, and the supplier a job reference. These identifiers are all useful, but they need a durable correlation model. The initiating request should create or receive an enterprise transaction identifier that is carried through every synchronous call, asynchronous message, retry, approval, and provider event.
Correlation does not mean copying complete payloads into every log. Each system should retain its own authoritative record and publish only the identifiers, versions, timestamps, states, and reasons needed to reconstruct the journey. The correlation record should connect the caller, source facts, CCA decision, locked authorization, BCM order, provider reference, BOC exception, and final operational reconciliation.
Make CCA Decisions Observable
A CCA decision should be more informative than approved or denied. It should identify the subject and delegation context, legal entity, card program, authoritative field sources, selected template, quantity rule, approval route, destination policy, provider route, reason code, and the versions of policy and template applied. Sensitive values should be minimized, but the governing logic must remain explainable.
Decision observability enables precise investigation. If two similar employees receive different outcomes, operations can determine whether the difference came from role, geography, employment status, source freshness, policy effective date or an approved exception. If the difference is unintended, the correction belongs in the authoritative source, CCA policy or approved mapping rather than in a downstream order patch.
Trace the Governed Request to Delivery Journey
- The consumer authenticates and submits the minimum identity and business context with a correlation identifier.
- The gateway records caller identity scope route traffic decision latency and trace identifier without logging unnecessary personal data.
- The integration layer records source references mapping version transformations queue state and retry history.
- CCA resolves authoritative fields and applies eligibility template approval quantity destination and provider policy.
- CCA records an explainable decision and issues a locked versioned authorization when the request is approved.
- BCM acknowledges the authorization idempotently and records proof order production shipment and delivery states.
- Provider adapters preserve original events normalize lifecycle meanings and correlate them to the BCM order.
- BOC detects missing, delayed contradictory or failed events and assigns each material exception to an accountable owner.
- The completed transaction is reconciled to the original CCA decision with final status and closure evidence.
Observe Business Invariants
The strongest signals are based on invariants that should remain true regardless of which portal, source system, or supplier is connected. An ineligible enterprise identity standardization must not create an executable order. An unapproved field must not reach the printed artifact. A retired template must not be released. A quantity above policy must require the correct approval. One CCA authorization must not create two physical orders. A terminal provider outcome must reconcile to the originating decision.
Each invariant should have a measurable signal, owner and response. Some can be enforced synchronously, such as rejecting a non-permitted template. Others require reconciliation, such as detecting that a supplier produced a quantity different from the authorized value. Observability turns these controls into continuously testable operating expectations instead of assumptions.
Use Metrics That Reflect Enterprise Control
| Metric group | Examples | Why it matters |
|---|---|---|
| Access | Registered consumer coverage denied scopes expired credentials and anomalous request rate | Shows whether only approved callers reach CCA capabilities |
| Decision | CCA approvals and denials by reason source conflicts stale data and exception use | Shows how enterprise policy controls demand |
| Integrity | Authorization-to-order mismatch duplicate prevention template-version mismatch and altered fields | Shows whether BCM executes the CCA decision intact |
| Lifecycle | Proof aging production delay event completeness shipment delay delivery failure and cancellation status | Shows whether authorized work progresses through fulfillment |
| Migration | Traffic by API version mapping errors semantic decision differences and deprecated consumer use | Shows whether integration change preserves governance |
| Reconciliation | Matched transactions unresolved exceptions time to owner time to closure and evidence completeness | Shows whether BOC can account for every material outcome |
Instrument Denials and Exceptions Carefully
A denial is often a successful control outcome rather than a system error. CCA may deny a request because the worker is not eligible, the card program is unavailable, an identity source is stale, a quantity exceeds policy, or an approval is missing. Those outcomes should be visible by reason and context without exposing unnecessary personal information. Repeated denials may reveal unclear portal guidance, source quality problems, or a policy defect.
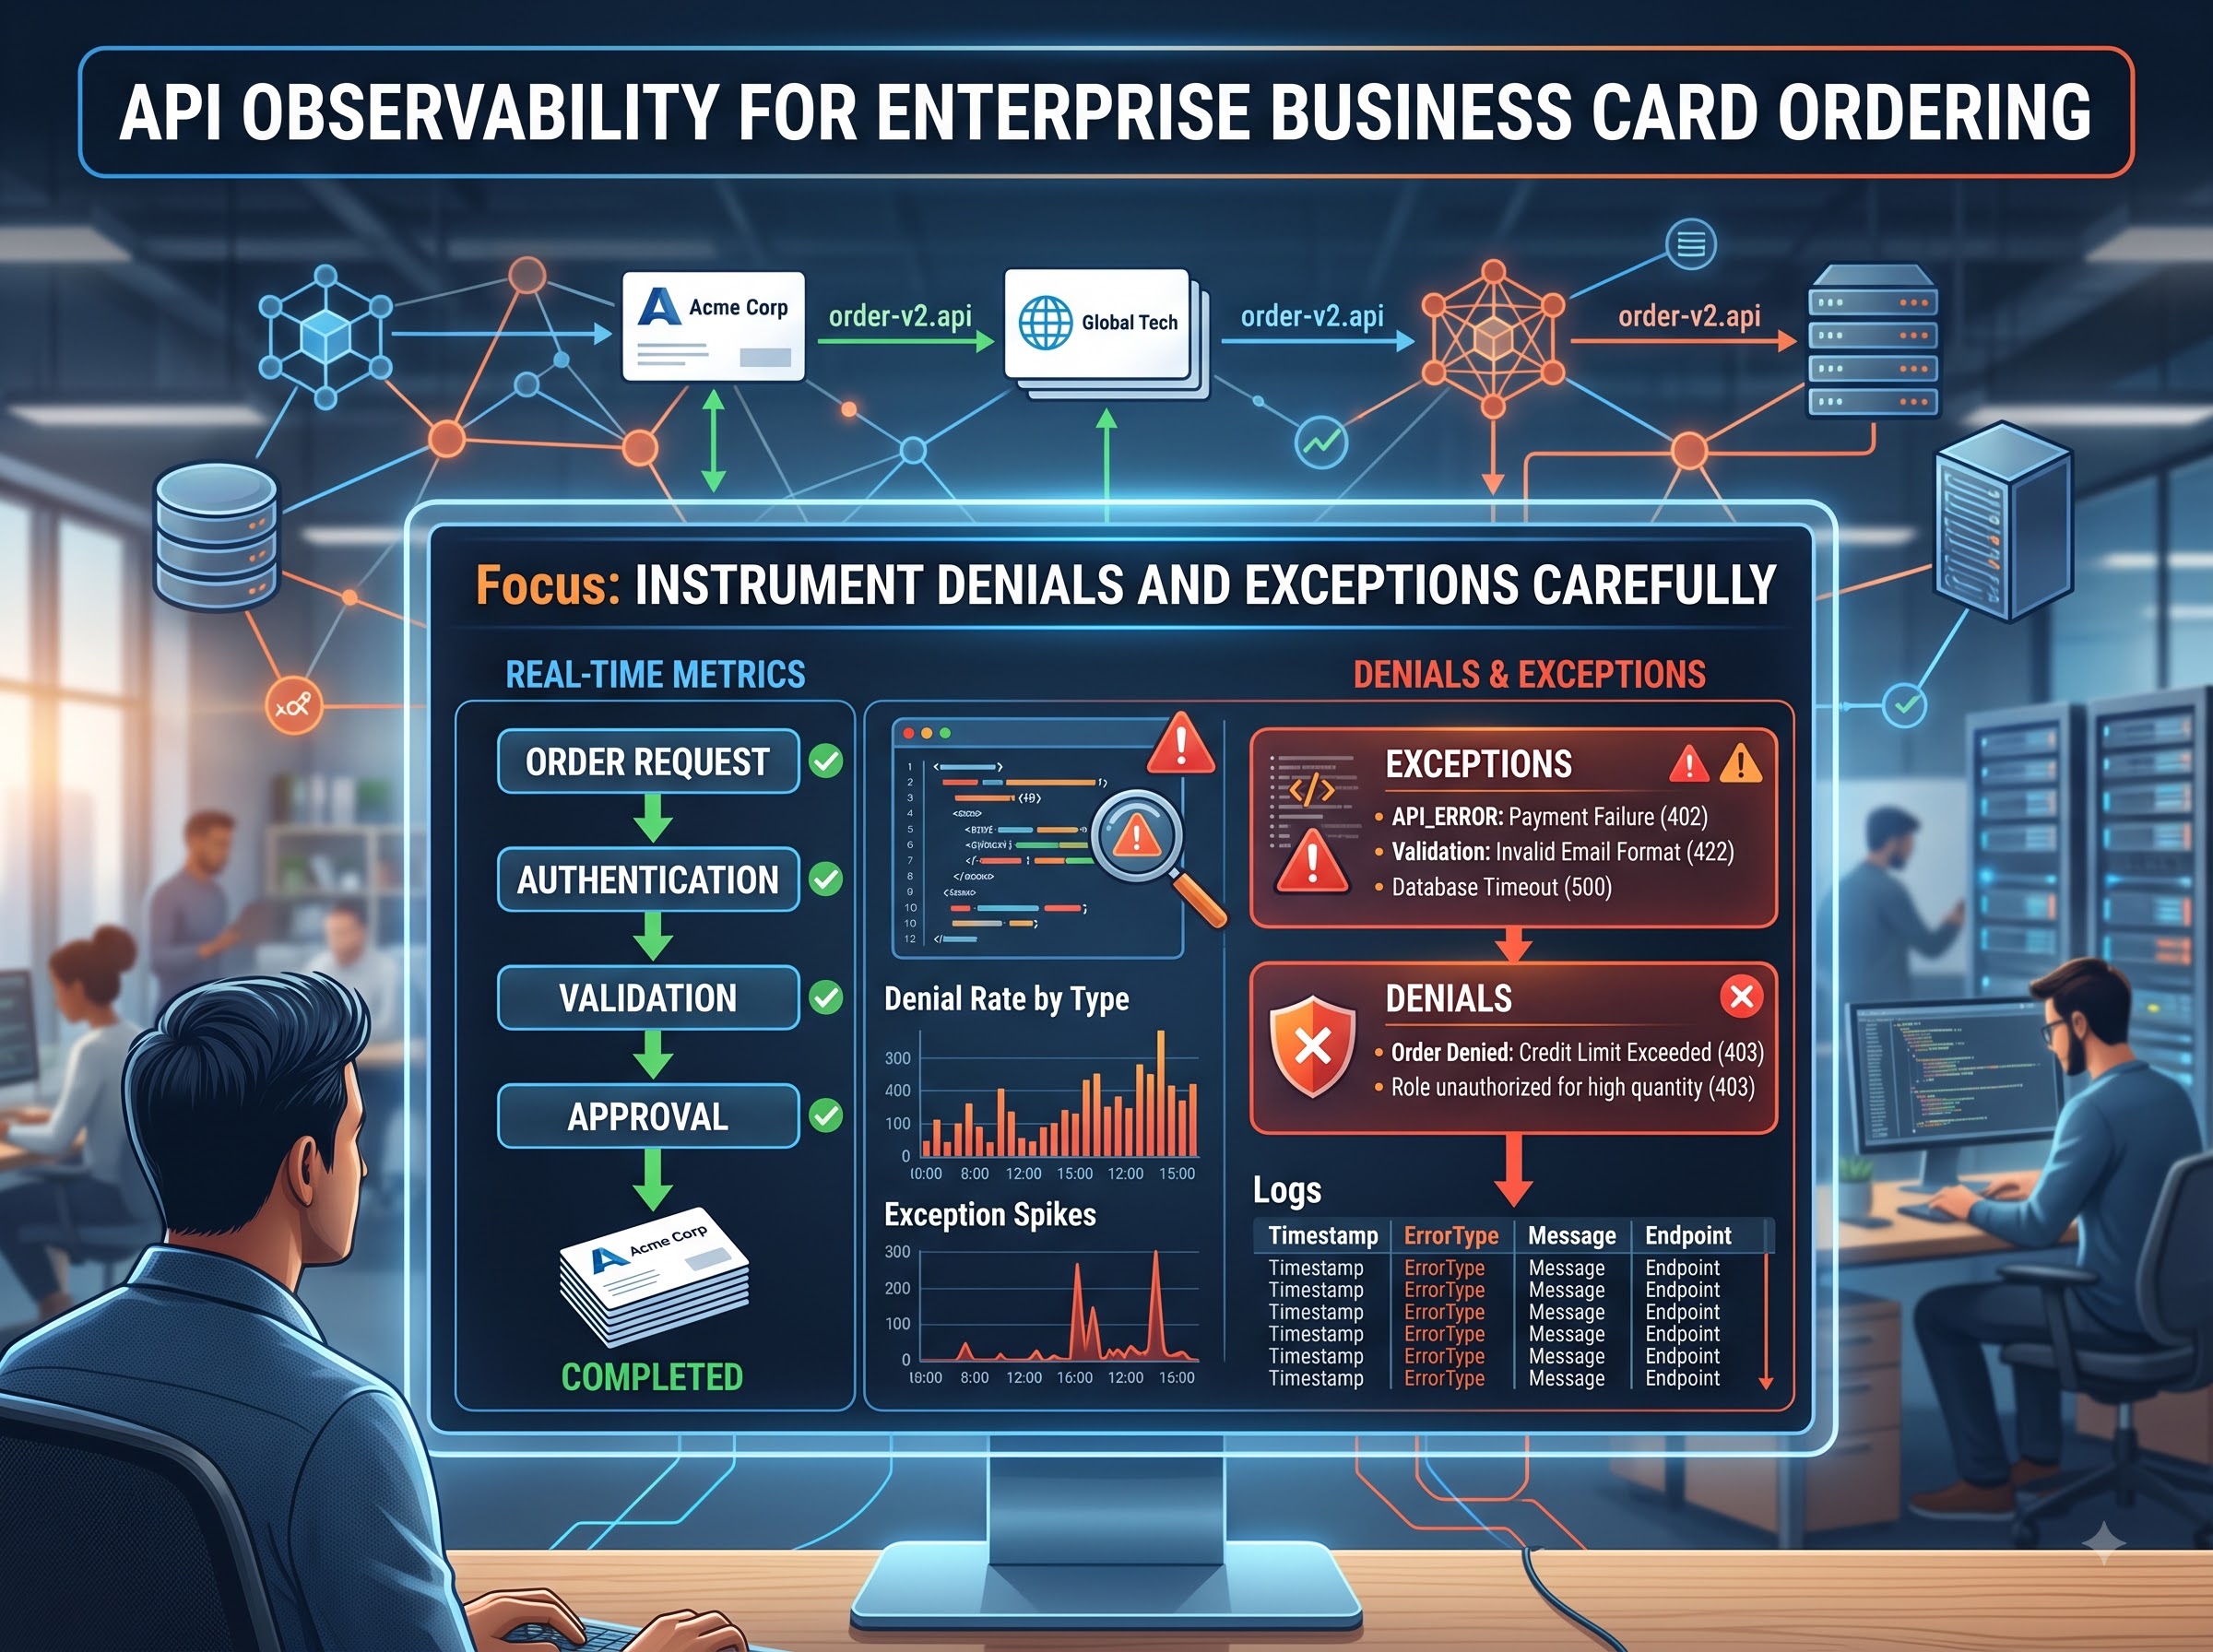
Exceptions begin when a standard path cannot be completed or evidence conflicts. BOC should receive a categorized exception with transaction identifiers, impact, owner, next action, due date, and closure criteria. The observability system should distinguish a retriable technical failure from an enterprise governance platform conflict that requires human review. Automated retries must not hide a wrong decision or create duplicate production.
Design Alerts Around Actionable Ownership
Alerts should describe a condition that a named team can act on. Security teams own credential anomalies, denied scopes, and suspicious traffic. Integration teams own mapping failures, queue backlogs, and contract incompatibilities. Data stewards own authoritative source conflicts. CCA owners handle unexpected decision patterns and policy defects. BCM operations own execution failures, while BOC coordinates cross-system exceptions and verifies closure.
Thresholds should reflect business impact. One rejected low-risk test transaction may need only a record, while a sudden increase in current-template mismatches demands immediate action. Alert grouping should prevent hundreds of messages for one underlying outage. Escalation should consider affected entities, card programs, providers, transaction volume, and whether physical production can still be stopped.
Preserve Privacy in Logs, Traces, and Dashboards
Business card processes involve identity and contact fields, but observability platforms should not become uncontrolled copies of workforce data. Logs should favor opaque identifiers, field classifications, source references, hashes, versions, reason codes, and status values. Full payload capture should be exceptional, access-restricted, time-limited and justified by a defined diagnostic purpose.
Masking must be applied before data leaves the originating service. Access to traces, dashboards and exports should follow least privilege and be reviewed regularly. Retention should reflect operational, audit and legal needs rather than default platform settings. When data is deleted from the authoritative transaction according to policy, derived observability stores should not silently preserve it indefinitely.
Observe the CCA to BCM Handoff
The authority-to-execution boundary deserves dedicated monitoring. CCA should produce a locked authorization with approved fields, template, quantity, destination, provider route, approvals, expiration, policy version, template version and decision identifier. BCM should acknowledge the same package, calculate or verify its integrity value and reject alterations. The observable comparison should confirm that nothing material changed between authorization and order creation.
Idempotency signals are equally important. A timeout may cause a consumer to retry even though BCM accepted the order. Stable keys and acknowledgments should show whether a retry was safely recognized, rejected or reconciled. Cancellation and reprint events must connect to the same authority model so operational urgency does not become an ungoverned alternate business card ordering path.
Monitor Webhooks and Asynchronous Events
Proof, production, shipment, delivery, cancellation and reprint states often arrive through webhooks or message queues. Observability should record sender identity, signature result, event type, event version, occurrence time, receipt time, replay result, correlation identifiers and normalization outcome. Duplicate and out-of-order events should be visible without generating false state transitions.
Event completeness is a business measure. If BCM records an order but no provider acknowledgment arrives within the expected window, BOC needs an owned exception. If a delivery event arrives without a matching authorization, it may indicate an integration or supplier defect. Monitoring should preserve the original event reference while reporting a normalized lifecycle that enterprise teams can compare across providers.
Build Service Level Objectives for the Whole Journey
Component-level targets remain useful, but they should support journey-level objectives. A portal can be available while CCA decisions are delayed by stale source data. A gateway can meet latency targets while approvals remain unowned. A provider can acknowledge orders quickly while delivery evidence is incomplete. The enterprise should define objectives for request decision time, approval aging, authorization-to-order acknowledgment, proof completion, production progress, event completeness, exception ownership and reconciliation.
Error budgets should not permit governance bypass. If a dependency is unavailable, the safe response may be to queue the request or present a controlled status. Reusing stale eligibility, accepting an expired approval or routing around CCA may improve apparent availability while weakening enterprise control. Continuity procedures need explicit risk limits, expiration and retrospective reconciliation.
Security and Audit Requirements
| Control area | Observability requirement | Evidence retained |
|---|---|---|
| Identity | Distinct service identities and authenticated event senders | Owner credential class environment and last use |
| Authorization | Gateway scope plus contextual CCA decision | Scope outcome decision reason and policy version |
| Integrity | Locked authorization idempotency and correlated state transitions | Hash order ID acknowledgment and lifecycle history |
| Privacy | Minimized fields, masking, access control, and time-bound retention | Data class access review export record and deletion result |
| Change | Versioned dashboards, alert mappings, contracts, and policies | Approval test effective date deployment and rollback |
| Audit | Searchable end-to-end evidence with restricted export | Query purpose requester, time range, and reconciliation result |
Implementation Roadmap
- Inventory consumers, gateway integration flows CCA services BCM transactions provider adapters BOC queues and current monitoring.
- Define the enterprise transaction identifier and map every local identifier and lifecycle state to it.
- Document CCA business invariants and create observable signals for eligibility identity template approval quantity routing and exceptions.
- Separate technical health governance health execution health and reconciliation views with accountable owners.
- Instrument CCA decisions with reasons source references policy versions template versions and privacy-safe context.
- Protect and monitor the locked CCA-to-BCM authorization including integrity idempotency acknowledgment and expiration.
- Secure webhook telemetry normalize provider events and establish completeness windows for each lifecycle stage.
- Create actionable alerts with severity routing escalation and closure evidence instead of generic error notifications.
- Validate dashboards using negative duplicate stale delayed out-of-order and mismatched end-to-end scenarios.
- Review metrics privacy retention access alert quality and unresolved exceptions through a recurring governance forum.
Frequently Asked Questions
What is business card API observability?
It is the ability to trace and explain the technical, governance and operational state of a business card transaction across connected systems.
How is observability different from API monitoring?
Monitoring usually measures availability, latency and errors. Observability connects those signals to CCA decisions, BCM execution and BOC reconciliation so the enterprise can explain the outcome.
What should CCA record for an authorization decision?
CCA should retain the decision identifier, reason, relevant authoritative sources, policy version, template version, approvals and the permitted execution parameters.
Should logs contain full business card payloads?
Normally no. Logs should use identifiers, classifications, versions, reasons and states. Full payload capture should be exceptional, restricted and time-limited.
How does BCM support observability?
BCM acknowledges the locked authorization, preserves idempotency and returns correlated proof, order, production, shipment and delivery states without changing CCA policy.
What is the role of BOC?
BOC monitors lifecycle completeness, assigns exceptions, tracks service levels, and reconciles execution outcomes to the original CCA decision.
Is a CCA denial an API error?
Not necessarily. A denial may be the correct policy outcome. It should be measured by reason and investigated when patterns indicate poor data, unclear guidance, or a policy issue.
What is the most important observability foundation?
A canonical transaction identity that connects the caller, CCA decision, BCM order, provider events, BOC exceptions, and final reconciliation.
The Strategic Outcome
CCA-centered observability lets enterprises see more than whether APIs are running. It shows whether business card authority was applied correctly, whether execution matched the authorized identity and design, and whether the operational result can be reconciled. Technical teams gain traceability without turning gateways or dashboards into shadow policy engines. Business owners gain evidence without depending on manual reconstruction.
The result is a connected ordering ecosystem that remains accountable at scale. CCA continues to control eligibility, identity, templates, approvals, quantity, and routing. BCM converts that decision into a controlled transaction. BOC ensures that missing events, failures, and mismatches have owners and closure evidence. Observability supports the CCA website purpose because it makes centralized governance measurable in every channel.
Select one high-volume business card journey and attempt to trace it from the authenticated consumer to the final delivery event. If the team cannot identify the CCA decision, policy version, locked BCM authorization, provider lifecycle, and BOC reconciliation from one transaction identity, observability has not yet reached the level required for enterprise governance.